Lazarus Alliance GovRAMP Assessments: 7 SLED Must-Dos

Lazarus Alliance GovRAMP Assessments: 7 SLED Must-Dos

Contrarian view: GovRAMP is not just another badge for cloud vendors. For SLED buyers, it is becoming procurement infrastructure: a way to replace one-off questionnaires with reusable, NIST 800-53-based security assurance that can survive contract review, cyber insurance scrutiny, incident response, and public accountability. The organizations that win in this environment will not treat GovRAMP or StateRAMP as a paperwork exercise; they will engineer auditable cloud operations from architecture through continuous monitoring.

Read More

Lazarus Alliance NIST 800-53 Audit Evidence: 7 Proofs

Lazarus Alliance NIST 800-53 Audit Evidence: 7 Proofs

The hardest part of a NIST 800-53 audit is no longer proving that controls exist; it is proving that the evidence is current, complete, attributable, repeatable, and tied to the exact assessment objective. That distinction matters because NIST 800-53 control assessment has become the common language behind FISMA compliance, FedRAMP, GovRAMP, CJIS-aligned cloud assurance, IRS 1075, healthcare security programs, defense supply-chain assurance, and enterprise cyber due diligence.

At Lazarus Alliance, we see the same pattern across mature organizations: teams maintain policies, screenshots, tickets, logs, diagrams, risk registers, and scan results, yet still struggle when assessors ask, “How does this artifact prove the control is implemented and operating?” Evidence quality—not evidence volume—is what separates a defensible authorization package from a remediation backlog.

Read More

FedRAMP 20x Audits by Lazarus Alliance: 7 Cloud Moves

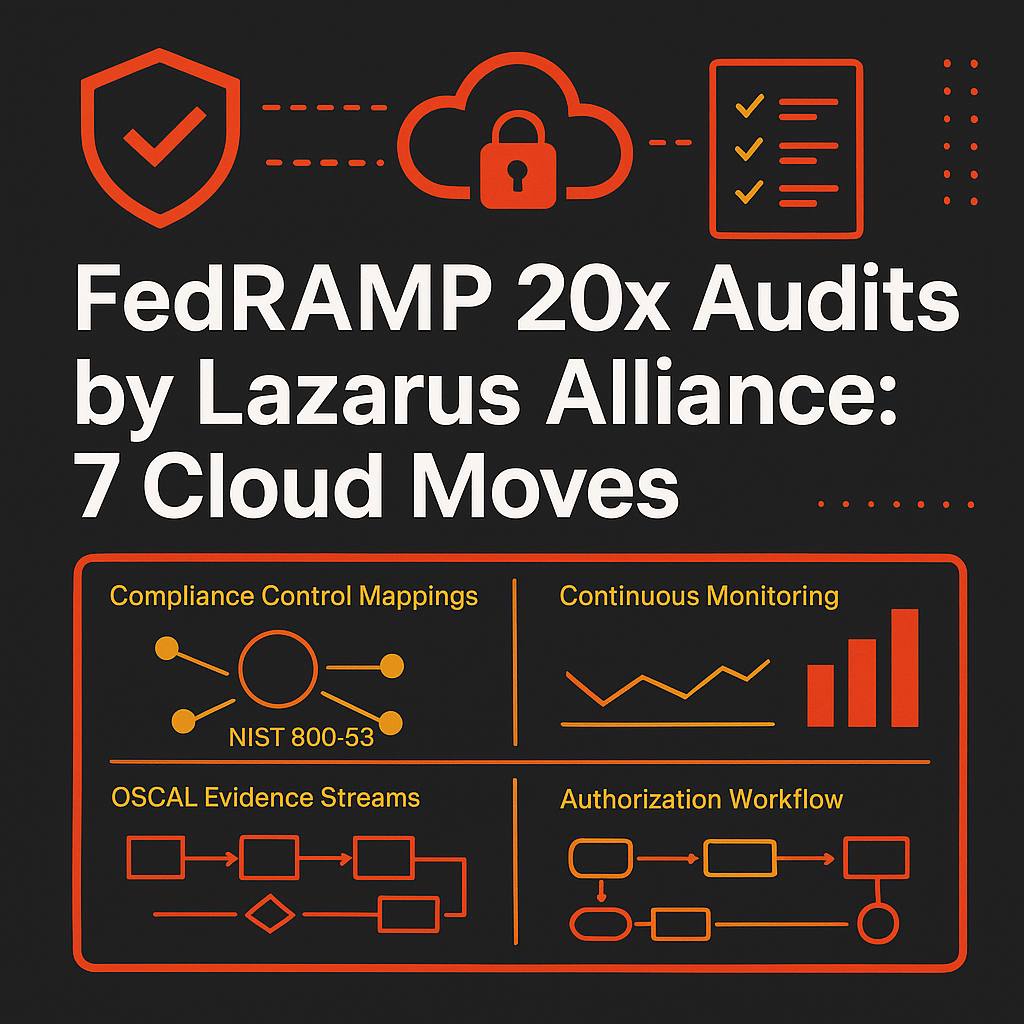
FedRAMP 20x Audits by Lazarus Alliance: 7 Cloud Moves

FedRAMP 20x is not merely a faster authorization path; it is a different evidence economy. The organizations that benefit most will not be the ones with the thickest System Security Plan. They will be the cloud service providers that can continuously prove control performance through structured, reusable, machine-readable evidence aligned to NIST 800-53, OSCAL, and real operational telemetry.

For federal cloud buyers, the shift is equally important. FedRAMP reported 92 new FedRAMP Certifications in FY2026, including 66 Rev5 and 26 FedRAMP 20x Certifications, and stated that the marketplace reached 538 FedRAMP Certified cloud service offerings; FedRAMP also said it will stop processing Legacy FedRAMP Rev5 Certification applications on June 11, 2027, according to FedRAMP, “Scaling a Better Path to Cloud Security”. That means the practical question for CISOs, compliance leaders, and cloud engineering teams is no longer “How do we assemble a package?” It is “How do we operate an assurance pipeline?”

Lazarus Alliance approaches FedRAMP 20x audits as a continuous cloud assurance program: control architecture, evidence automation, technical validation, governance, and assessor-ready traceability. The following seven cloud moves translate FedRAMP 20x into an actionable operating model for providers pursuing federal authorization, agencies evaluating cloud risk, and enterprises seeking NIST 800-53-grade assurance.

Read More