Proactive Services - We Stop Threats Before They Become Obituaries.

Cybersecurity Audit & Compliance

Cybersecurity Audit & Compliance

Authorized CMMC C3PAO, FedRAMP 3PAO, SOC 2 & PCI DSS QSA assessments. Independent cybersecurity assessments designed for efficiency, clarity, and defensible compliance outcomes.

Independent Cybersecurity Assessments

Independent Cybersecurity Assessments

Lazarus Alliance provides independent cybersecurity assessments, audits, examinations, and certification services that help organizations demonstrate security and compliance. Our accredited and authorized professionals assess organizations against leading frameworks and standards, including CMMC, FedRAMP, SOC 1/2/3, PCI DSS, ISO, NIST, and other regulatory and industry requirements.

Original Cybersecurity Research

Original Cybersecurity Research

Lazarus Alliance Research publishes original, aggregate, and anonymized cybersecurity assessment and audit data derived from completed client engagements. Our benchmark research provides empirical insights into assessment duration, evidence requirements, common findings and exceptions, scope complexity, and other factors that influence cybersecurity compliance outcomes across CMMC, FedRAMP, SOC 2, and additional frameworks.

Government & Defense Cybersecurity

Government & Defense Cybersecurity

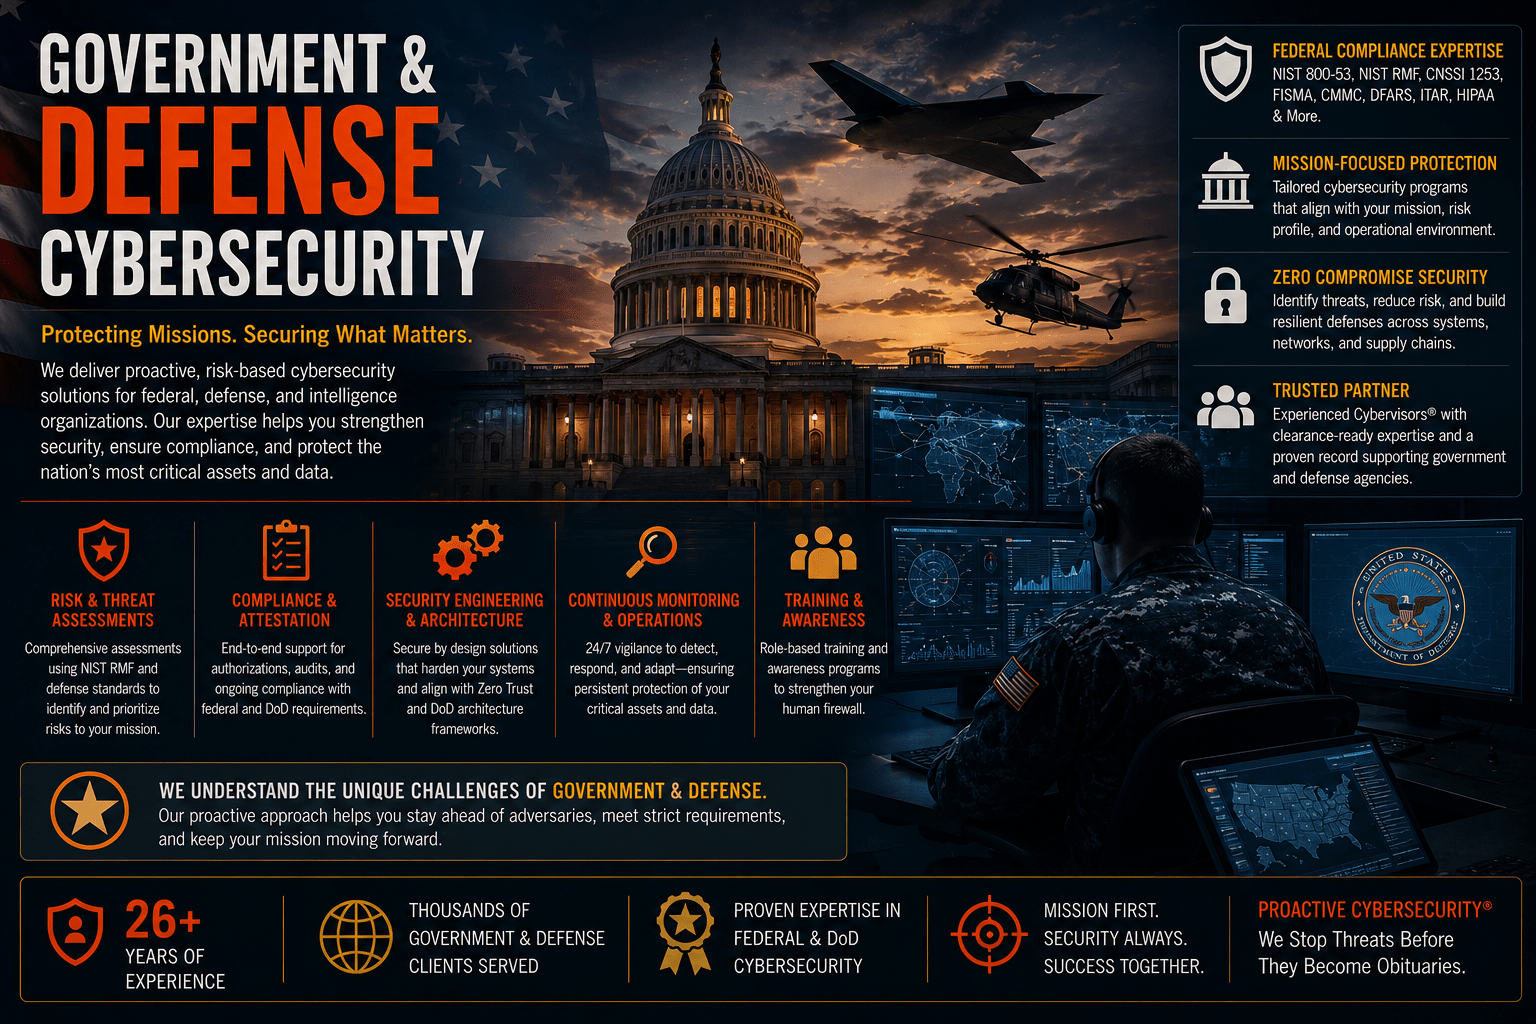
Lazarus Alliance helps federal agencies, defense contractors, cloud service providers, and organizations in the Defense Industrial Base navigate complex cybersecurity assessment and compliance requirements. Our expertise spans CMMC, FedRAMP, NIST SP 800-171, NIST SP 800-53, DFARS, FISMA, and other federal security requirements, combining independent assessment expertise with practical knowledge gained from real-world cybersecurity engagements.

Lazarus Alliance Research

Original cybersecurity audit, assessment, and compliance intelligence derived from aggregate, anonymized engagement data.

DatasetResearch DatasetBenchmark Report
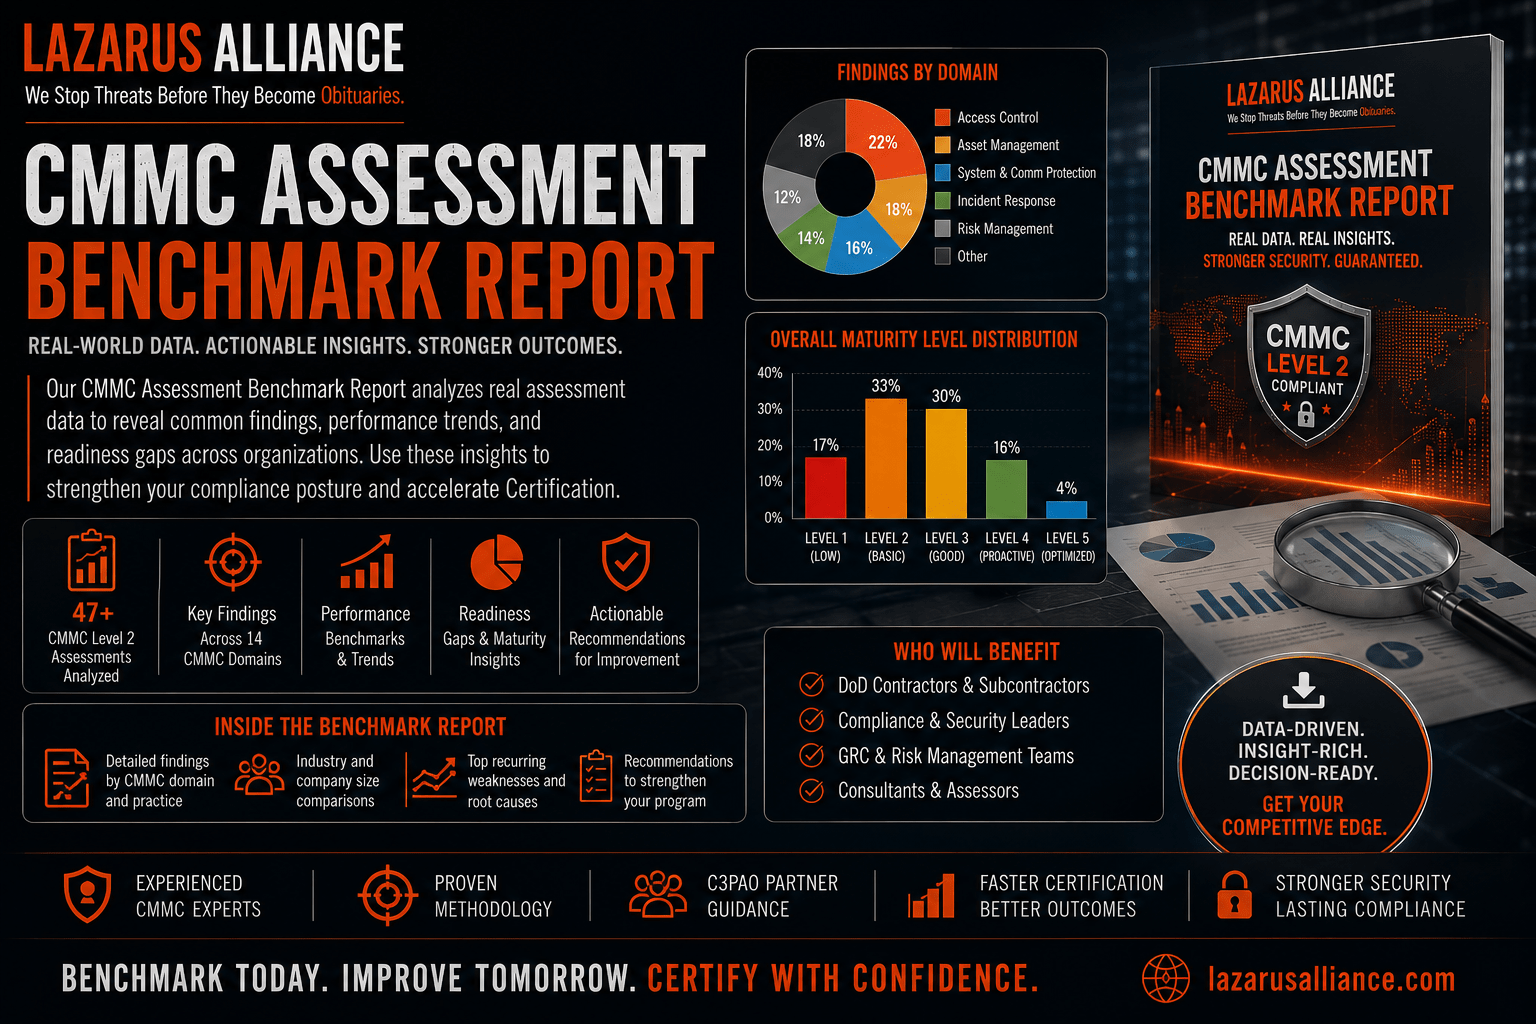
47Completed Formal CMMC Level 2 Assessments Analyzed
2026 CMMC Assessment Benchmark Report
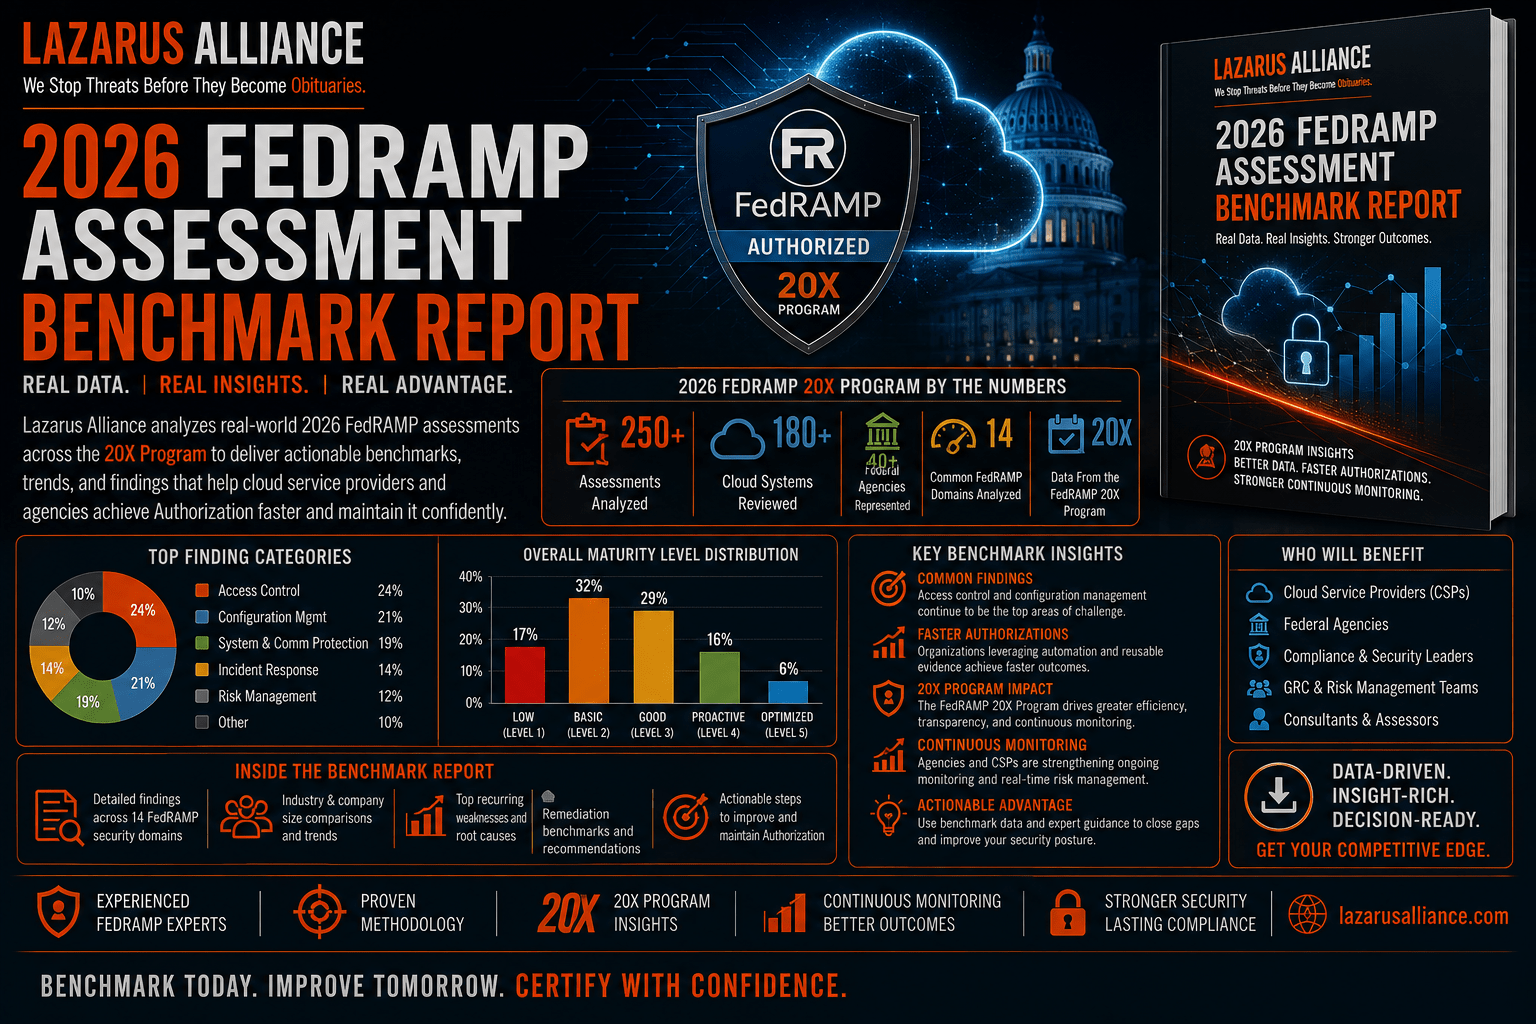
38Completed FedRAMP Assessments Analyzed
2026 FedRAMP Assessment Benchmark Report
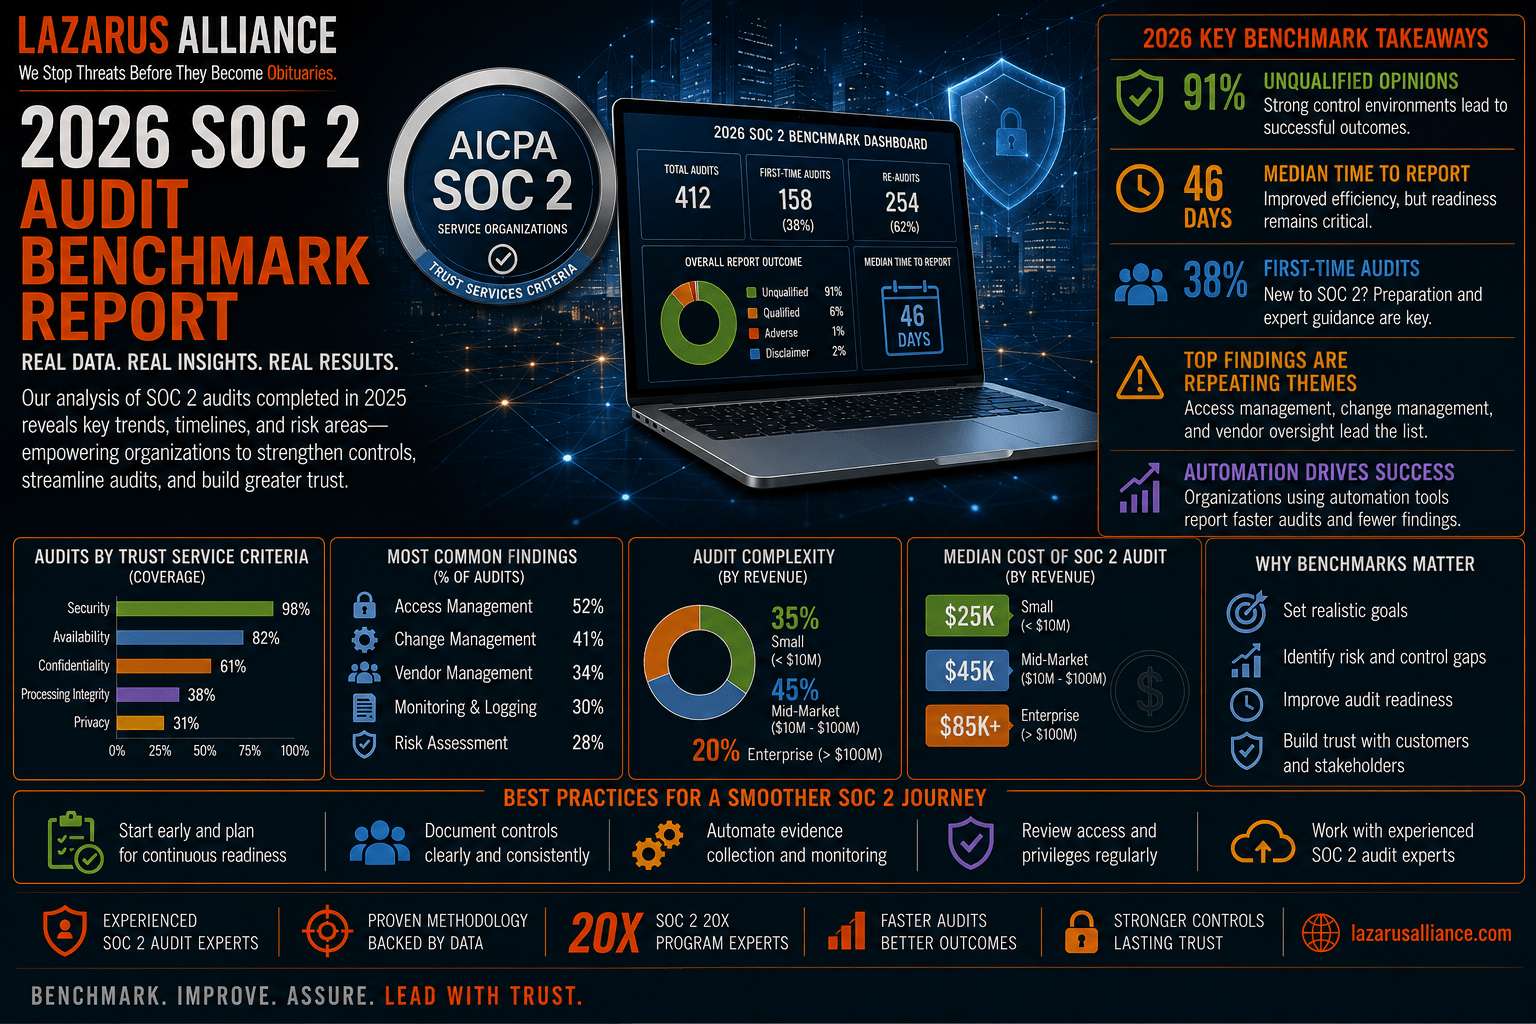
75Completed SOC 2 Assessments Analyzed
2026 SOC 2 Assessment Benchmark Report
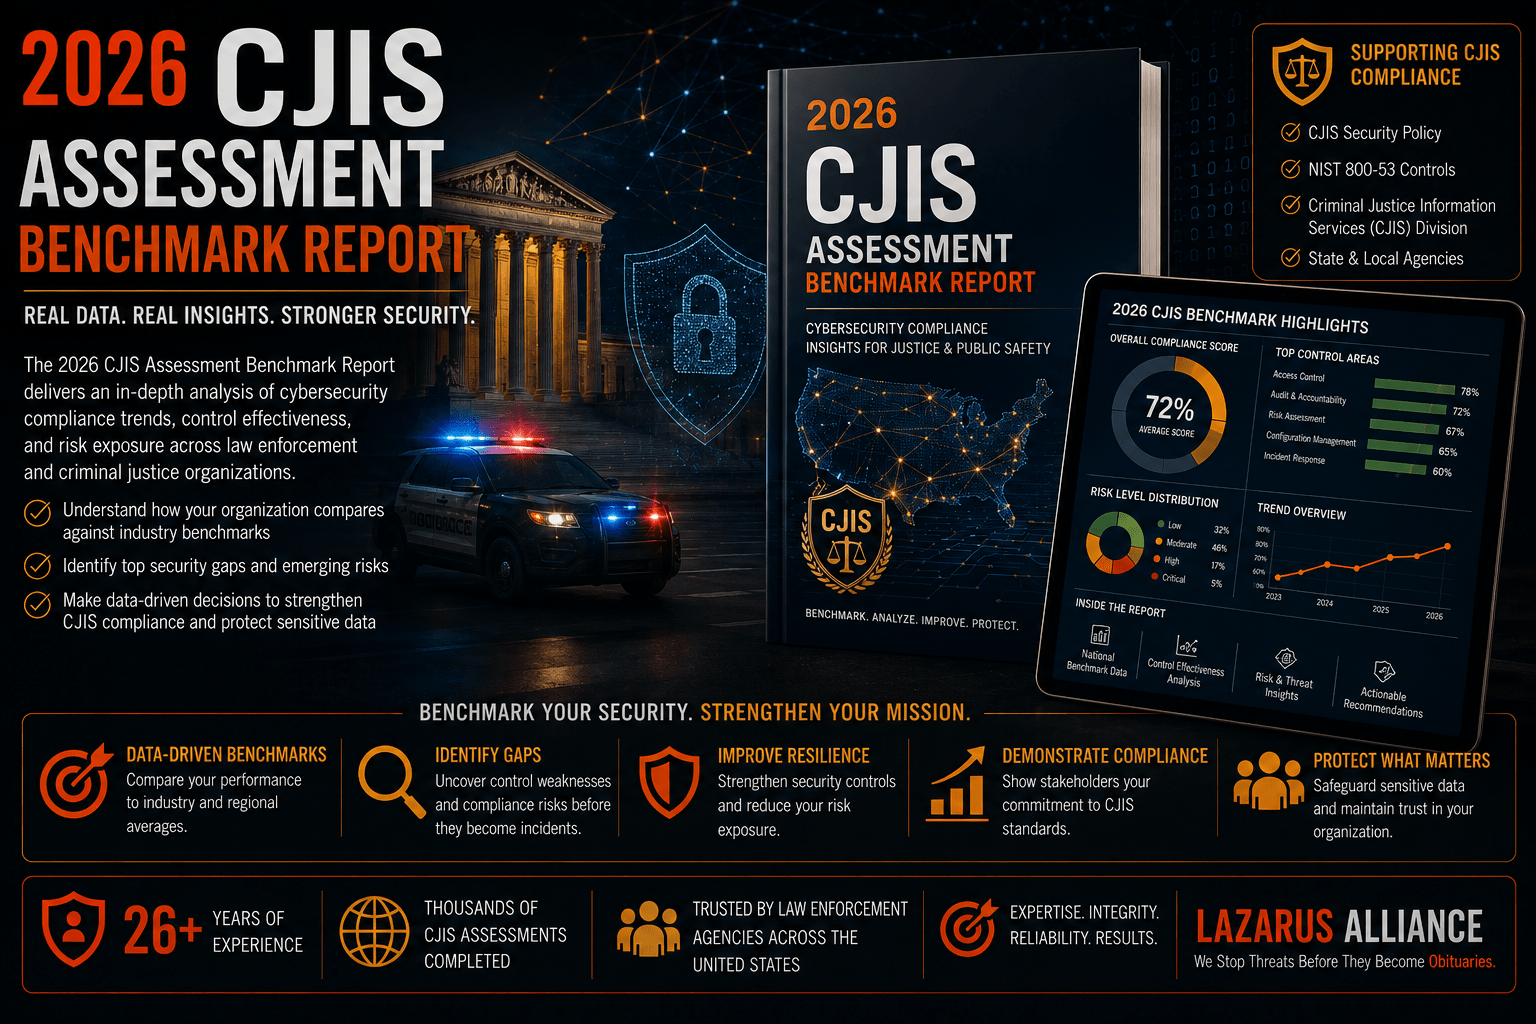
28Completed CJIS Assessments Analyzed
2026 CJIS Assessment Benchmark Report
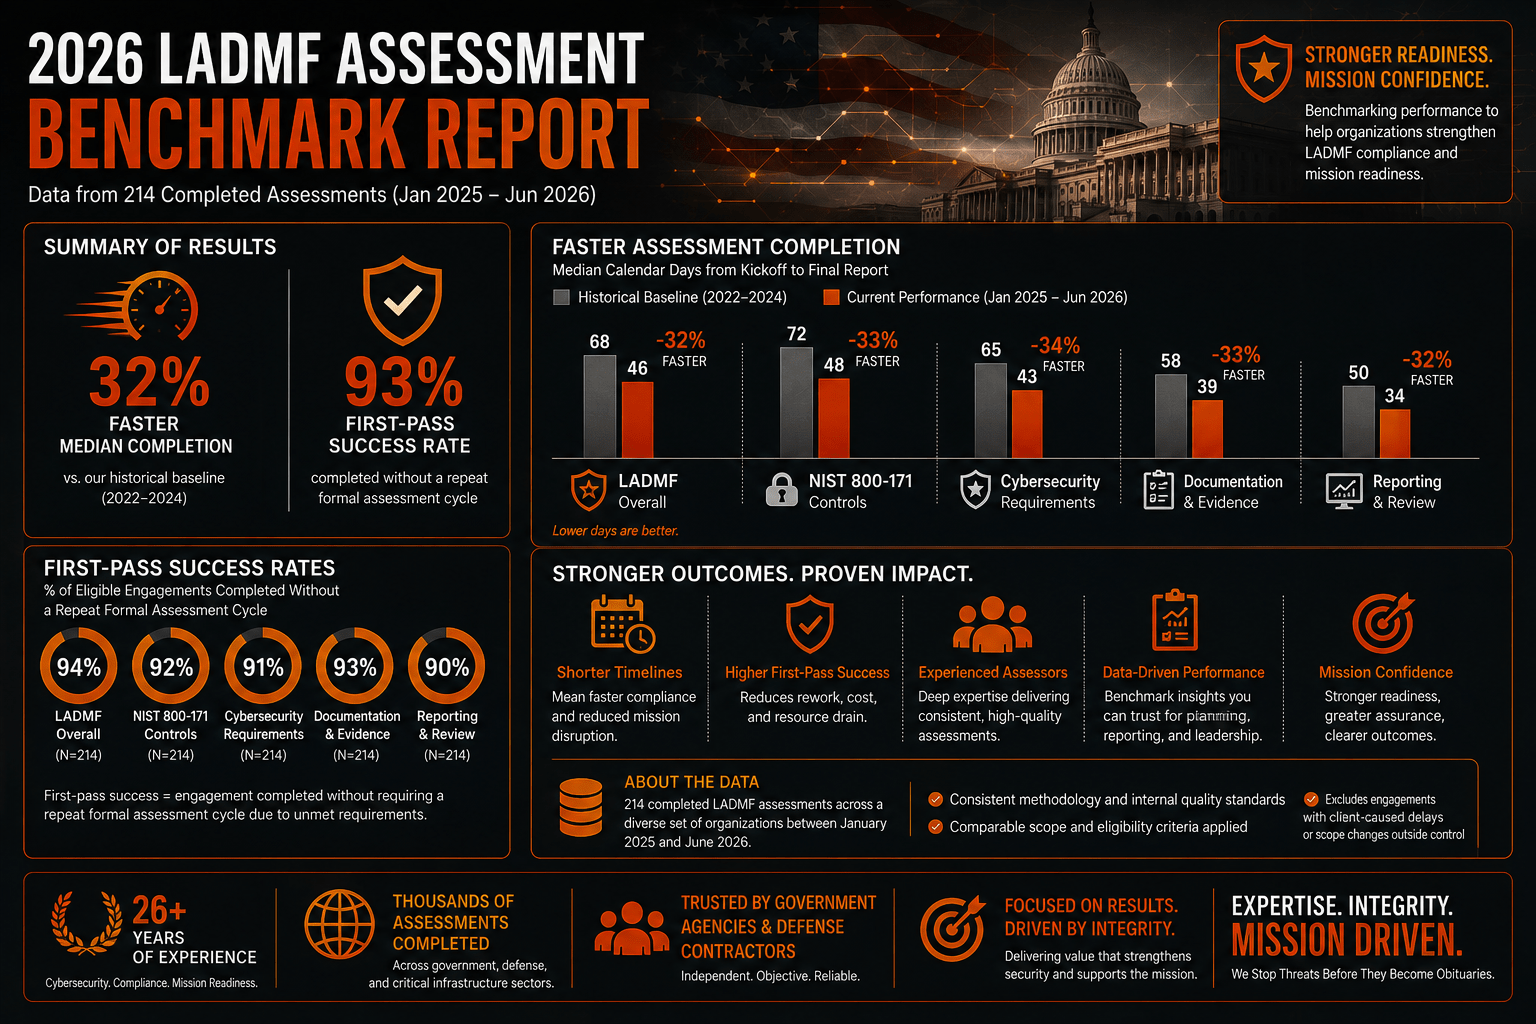
18Completed LADMF Assessments Analyzed
2026 LADMF Assessment Benchmark Report

Explore Lazarus Alliance Research →

Frequently Asked Questions

Lazarus Alliance is a veteran-owned global provider of Proactive Cybersecurity® services. For over 26 years, we have delivered audit, compliance, risk management, privacy, penetration testing, and governance solutions to organizations of all sizes across every industry and jurisdiction.

Proactive Cybersecurity® is our core philosophy of stopping threats before they become problems. We focus on continuous monitoring, real-time risk management, and building sustainable programs instead of reactive “check-the-box” audits.

Lazarus Alliance provides CMMC C3PAO assessments, FedRAMP 3PAO assessments, SOC 2 examinations, PCI DSS QSA audits, risk assessments, privacy impact assessments, vulnerability and penetration testing, policy and governance development, and Cybervisor® advisory services.

Call +1-888-896-7580 or complete the form on this page for a free, no-obligation consultation with one of our expert Cybervisors®.

Lazarus Alliance combines experienced assessment teams with structured evidence workflows and automation designed to improve assessment efficiency and evidence quality. Framework-specific benchmark results are published through Lazarus Alliance Research.

A Cybervisor® is our senior-level, AI-enhanced cybersecurity advisor who works as an extension of your team. They provide strategic guidance, hands-on implementation, and continuous support to accelerate compliance and strengthen your overall security posture.

Yes. We partner with organizations of all sizes, from startups to global enterprises like Cisco and Vanguard, across every major industry. Our efficient methodology makes compliance achievable without unnecessary complexity or cost.

Absolutely. We support clients worldwide with deep expertise in both U.S. and international regulations, including CCPA, PIPEDA, DPDP, and other global privacy and cybersecurity requirements.

Phone consultations: Monday–Friday, 8:00 AM–5:00 PM MST. Form and email inquiries receive a next-business-day response.

Expert Publications

Expert Publications deliver timely cybersecurity insights, regulatory analysis, and practical guidance from Lazarus Alliance experts on emerging threats, compliance requirements, industry developments, and evolving security standards.

FedRAMP 20x Audit: 6 Lazarus Alliance Cloud Wins for SaaS

FedRAMP 20x is not simply a faster audit lane; it is a forcing function for evidence engineering. SaaS providers that treat it as a document-submission exercise will recreate the same bottlenecks with newer labels. Providers that redesign control ownership, telemetry, and machine-readable evidence around NIST 800-53 will be better positioned for federal cloud authorization, GovRAMP, SOC 2, CMMC, CJIS, PCI DSS, HIPAA, IRS 1075, ISO 27001, C5, and LA DMF evidence reuse.

According to the FedRAMP PMO, FedRAMP 20x was launched to modernize cloud authorization after OMB’s modernization direction, reduce assessment burden, remove agency sponsorship barriers, encourage automation, and transition toward machine-readable interactions; FedRAMP also reported that 26 companies received limited pilot certifications and announced the first full FedRAMP 20x Class C Certification in 2026 FedRAMP PMO, Memo to Milestone. For SaaS executives, the practical takeaway is clear: authorization strategy now depends as much on data architecture and evidence pipelines as on policy binders.
Read More

6 NIST CSF 2.0 Governance Audits by Lazarus Alliance

Contrarian audit insight: most failed cyber risk programs do not fail because teams lack tools; they fail because cybersecurity governance cannot prove how decisions are made, funded, measured, and escalated. NIST CSF 2.0 changes that conversation by placing Govern alongside Identify, Protect, Detect, Respond, and Recover, making enterprise risk management a first-class cybersecurity function rather than an annual policy exercise, as reflected in NIST’s current draft guidance on ICT risk management and executive cybersecurity leadership NIST CSRC, Governing and Managing ICT Risk Programs Draft.

Read More

Lazarus Alliance CJIS Audits: 7 Vendor Compliance Fixes

The modernization of CJIS compliance is not just a law-enforcement technology issue; it is a vendor evidence issue. Agencies can no longer treat Criminal Justice Information as a data set that stays neatly inside agency-owned networks. Records management systems, cloud hosting providers, digital evidence platforms, mobile applications, outsourced support teams, analytics tools, and identity services may all touch CJI. The FBI CJIS Security Policy establishes security requirements for protecting Criminal Justice Information and related systems, and agencies remain accountable for ensuring that vendor environments are governed, tested, and auditable under that policy FBI, CJIS Security Policy Resource Center.

For CISOs, compliance officers, IT directors, and procurement leaders, the practical question is simple: can every vendor that stores, processes, transmits, supports, or administers CJI produce audit-ready evidence on demand? Lazarus Alliance CJIS audits focus on that evidence gap. The most mature agencies are aligning CJIS compliance with NIST SP 800-53 control language, enterprise vendor risk management, continuous monitoring, and multi-framework compliance assessments rather than waiting for a point-in-time scramble NIST, SP 800-53 Rev. 5.

Read More

CMMC Audit Readiness: 9 DFARS Risks Lazarus Alliance Finds

CMMC audit readiness is not a paperwork exercise; it is an evidence integrity exercise.

Lazarus Alliance repeatedly finds that defense contractors can describe their security program, but struggle to prove that the right controls operate on every system that processes, stores, or transmits Federal Contract Information (FCI) or Controlled Unclassified Information (CUI). Under DFARS 252.204-7021, contractors must have and maintain the required CMMC status for applicable information systems, complete an annual affirmation of continuous compliance in SPRS for each applicable CMMC UID, and flow down applicable CMMC requirements to subcontractors eCFR, 48 CFR 252.204-7021.

The contrarian reality: most CMMC failures begin long before an assessor reviews a control. They begin when scope is vague, the System Security Plan is not evidence-backed, cloud inheritance is overstated, subcontractor obligations are not verified, or leadership signs an SPRS affirmation without a repeatable evidence basis. This article summarizes nine DFARS compliance and NIST 800-171 evidence risks Lazarus Alliance commonly helps defense contractors resolve before formal assessment activity.

Read More

Awards and Accolades

Do you have any questions?

Lazarus Alliance is the premier global provider of Proactive Cybersecurity®, delivering direct access to top-tier experts in cyberspace law, IT security and operations, risk and governance, compliance, policy development, and related fields.