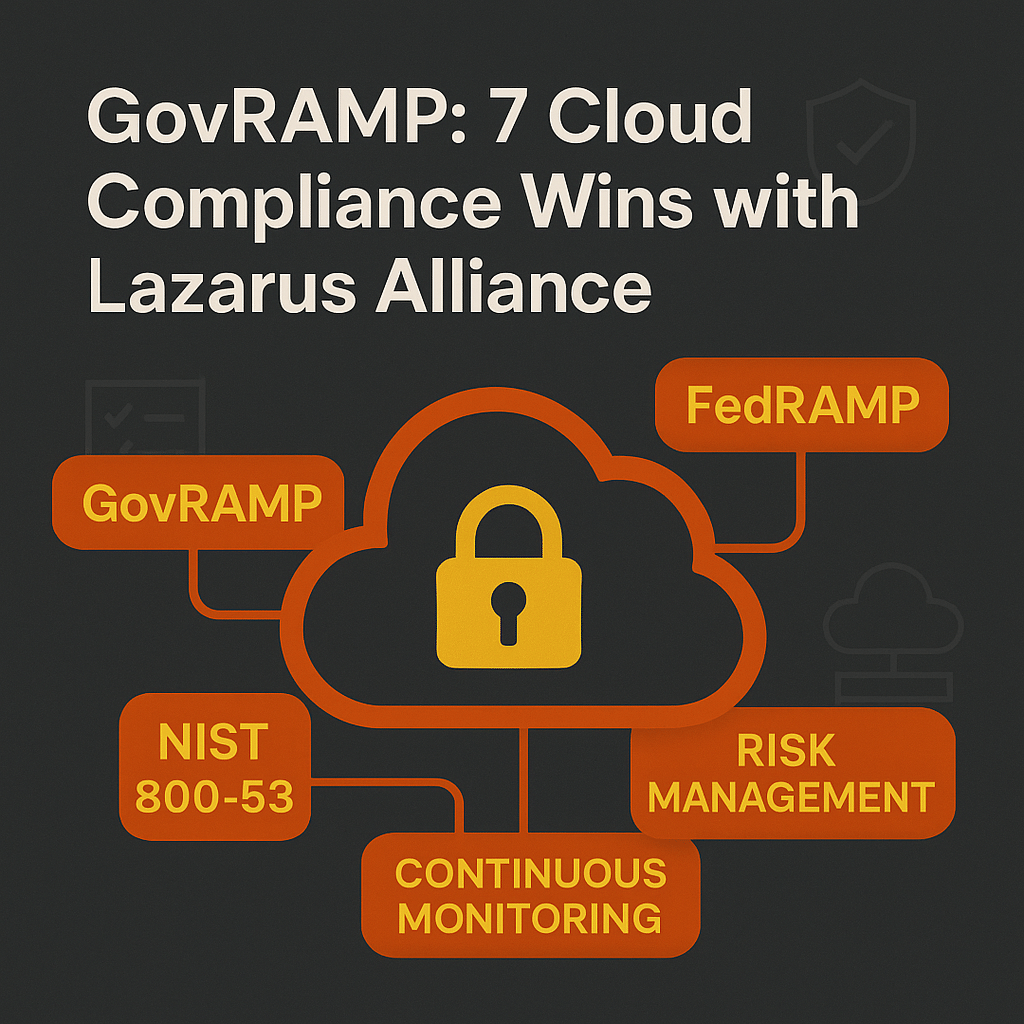
GovRAMP is not simply FedRAMP for state government. The real opportunity is more strategic: build one NIST 800-53-centered assurance program that can support public-sector procurement, FedRAMP reciprocity planning, CJIS conversations, SOC 2 customer assurance, PCI DSS segmentation, HIPAA safeguards, IRS 1075 data protection, and defense-sector overlays without restarting the audit process each time a buyer asks for evidence.
For cloud service providers, SaaS vendors, managed platforms, data analytics companies, and government technology suppliers, GovRAMP can become a commercial accelerator rather than a compliance bottleneck. Lazarus Alliance helps organizations translate cloud compliance requirements into assessor-ready evidence, practical risk management decisions, and repeatable cybersecurity audits aligned to the public-sector expectations that matter.