Proactive Services - We Stop Threats Before They Become Obituaries.

Cybersecurity Audit & Compliance

Cybersecurity Audit & Compliance

Authorized CMMC C3PAO, FedRAMP 3PAO, SOC 2 & PCI DSS QSA assessments. Independent cybersecurity assessments designed for efficiency, clarity, and defensible compliance outcomes.
Independent Cybersecurity Assessments

Independent Cybersecurity Assessments

Lazarus Alliance provides independent cybersecurity assessments, audits, examinations, and certification services that help organizations demonstrate security and compliance. Our accredited and authorized professionals assess organizations against leading frameworks and standards, including CMMC, FedRAMP, SOC 1/2/3, PCI DSS, ISO, NIST, and other regulatory and industry requirements.

Original Cybersecurity Research

Original Cybersecurity Research

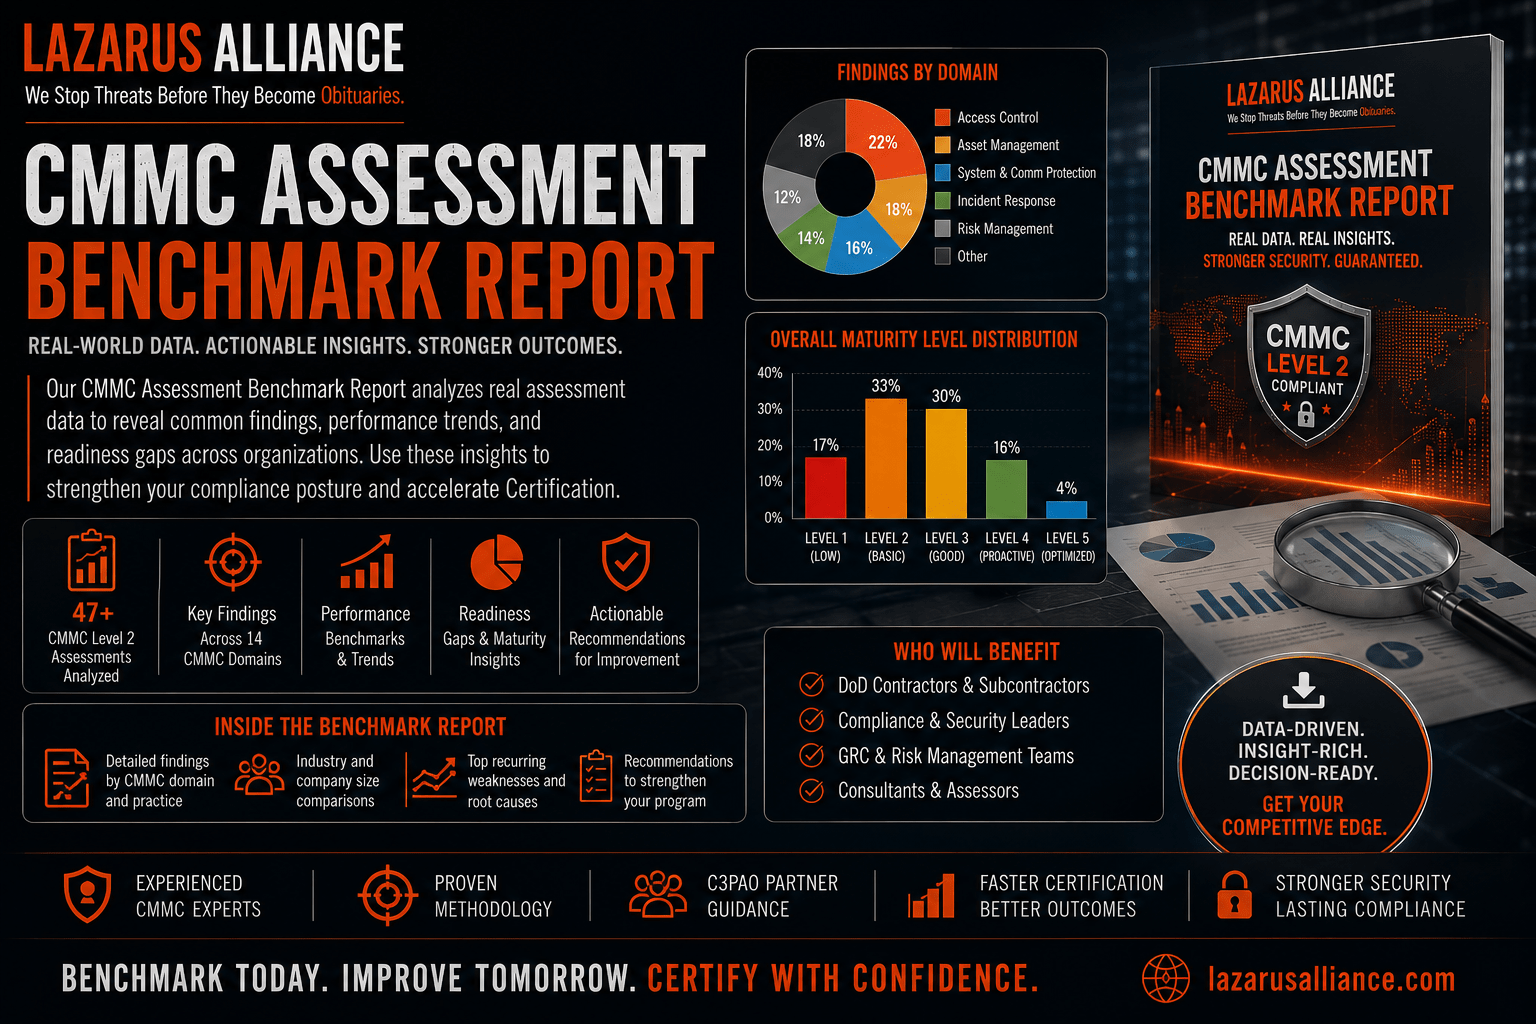
Lazarus Alliance Research publishes original, aggregate, and anonymized cybersecurity assessment and audit data derived from completed client engagements. Our benchmark research provides empirical insights into assessment duration, evidence requirements, common findings and exceptions, scope complexity, and other factors that influence cybersecurity compliance outcomes across CMMC, FedRAMP, SOC 2, and additional frameworks.

Government & Defense Cybersecurity

Government & Defense Cybersecurity

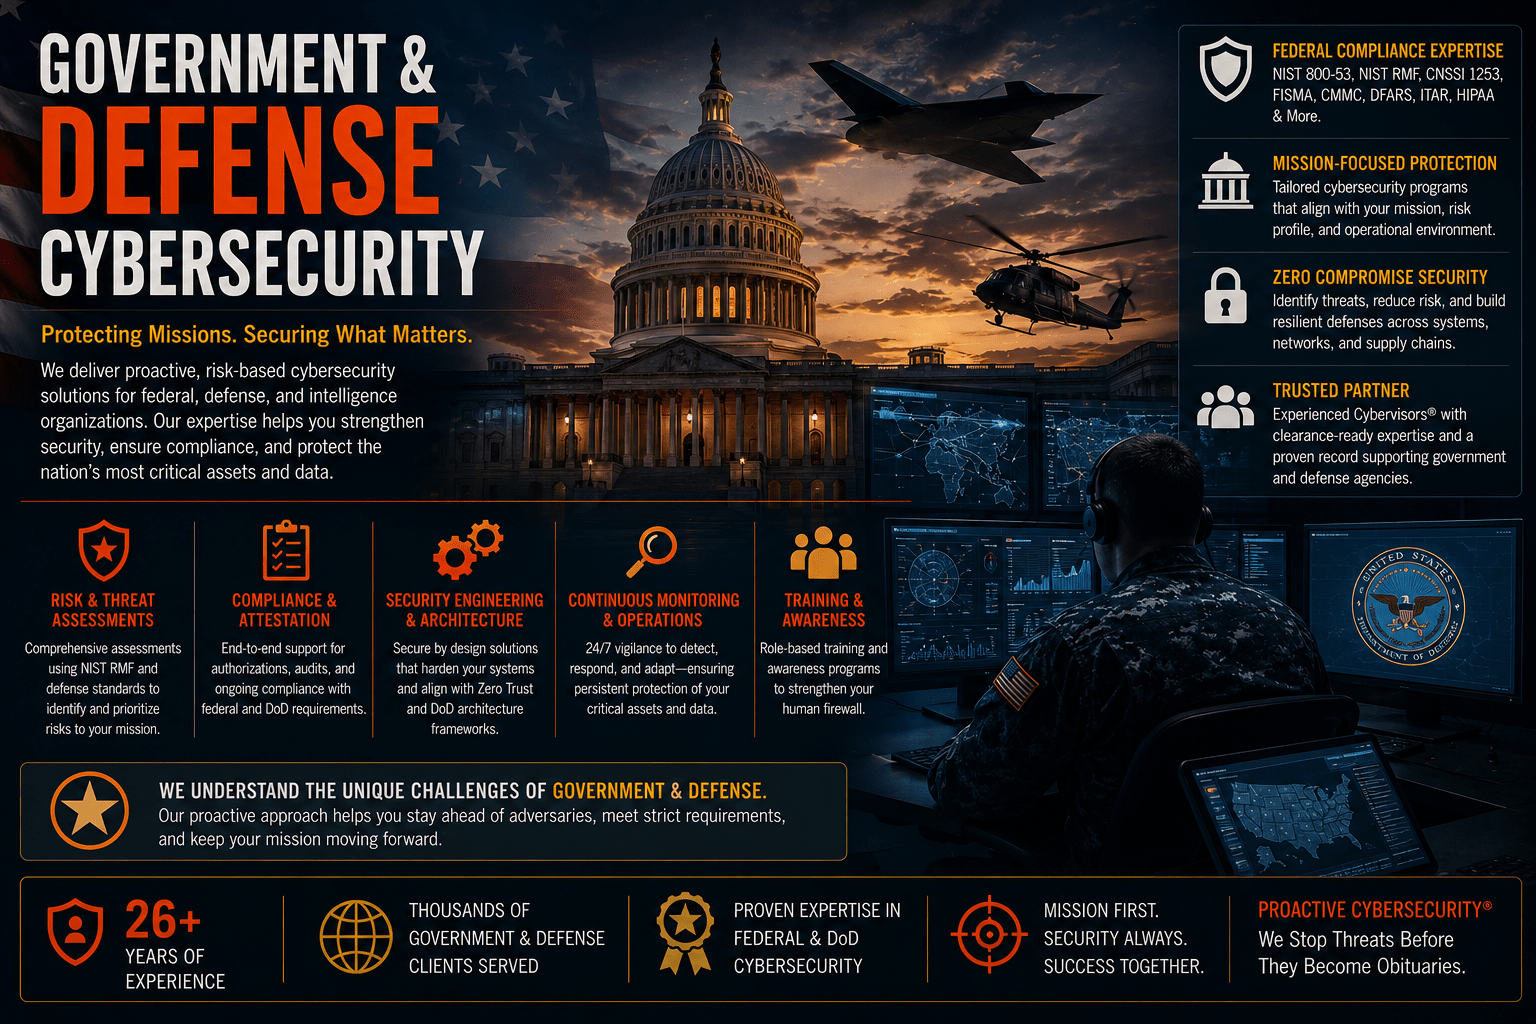
Lazarus Alliance helps federal agencies, defense contractors, cloud service providers, and organizations in the Defense Industrial Base navigate complex cybersecurity assessment and compliance requirements. Our expertise spans CMMC, FedRAMP, NIST SP 800-171, NIST SP 800-53, DFARS, FISMA, and other federal security requirements, combining independent assessment expertise with practical knowledge gained from real-world cybersecurity engagements.

Lazarus Alliance Research

Original cybersecurity audit, assessment, and compliance intelligence derived from aggregate, anonymized engagement data.

DatasetResearch DatasetBenchmark Report
47Completed Formal CMMC Level 2 Assessments Analyzed
2026 CMMC Assessment Benchmark Report
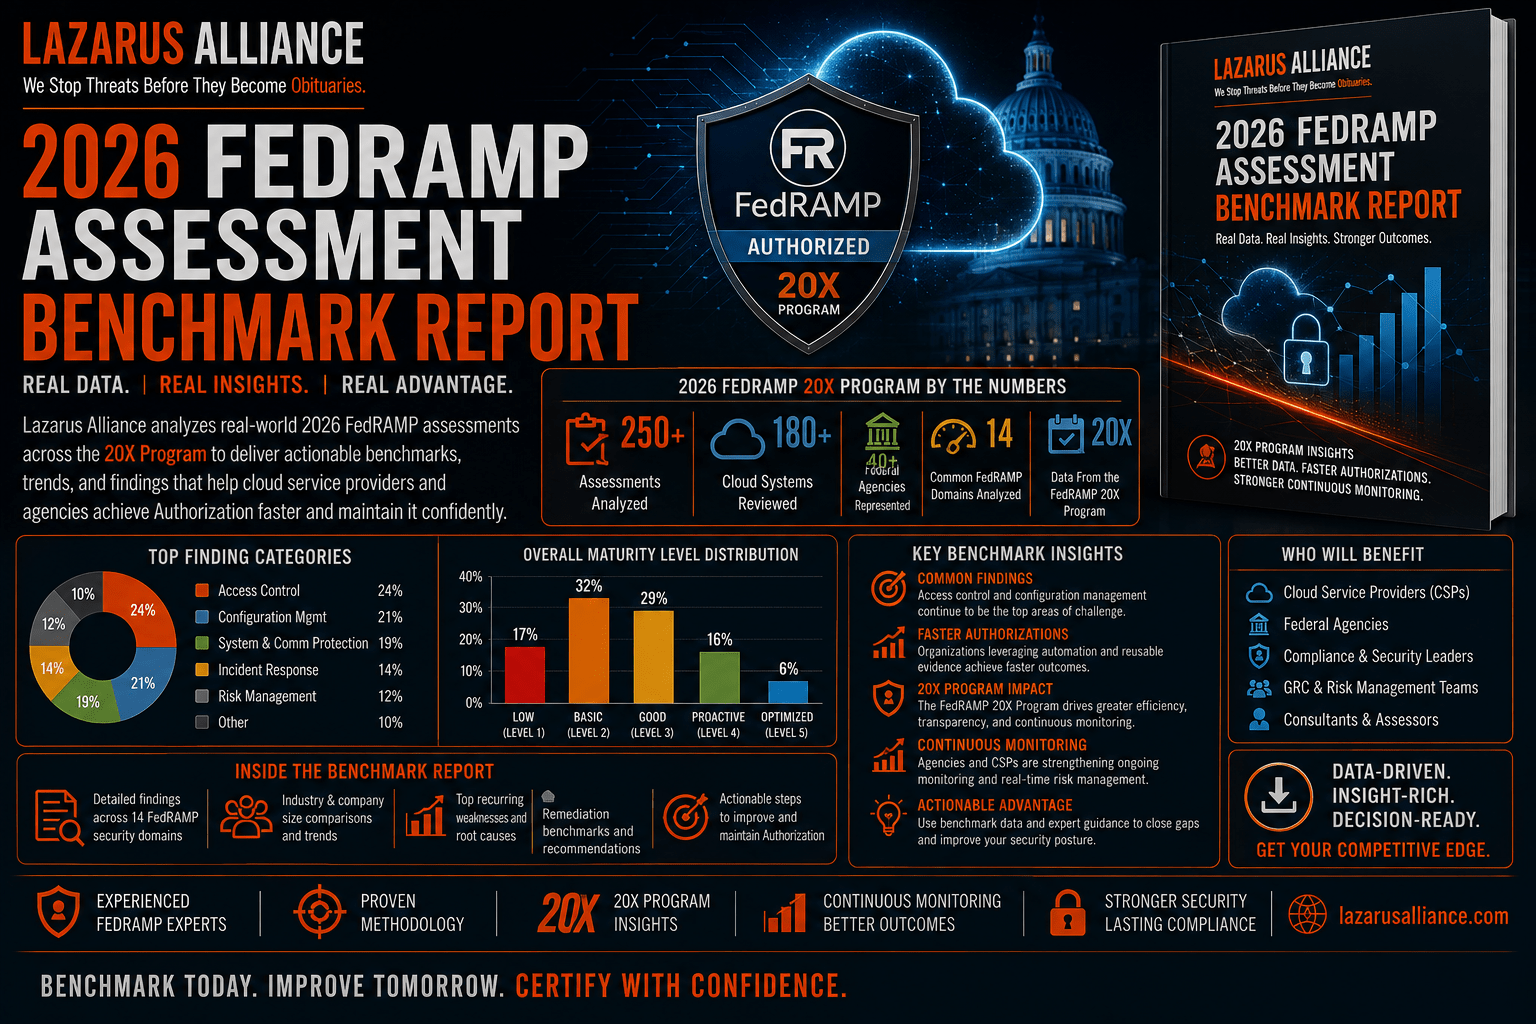
38Completed FedRAMP Assessments Analyzed
2026 FedRAMP Assessment Benchmark Report
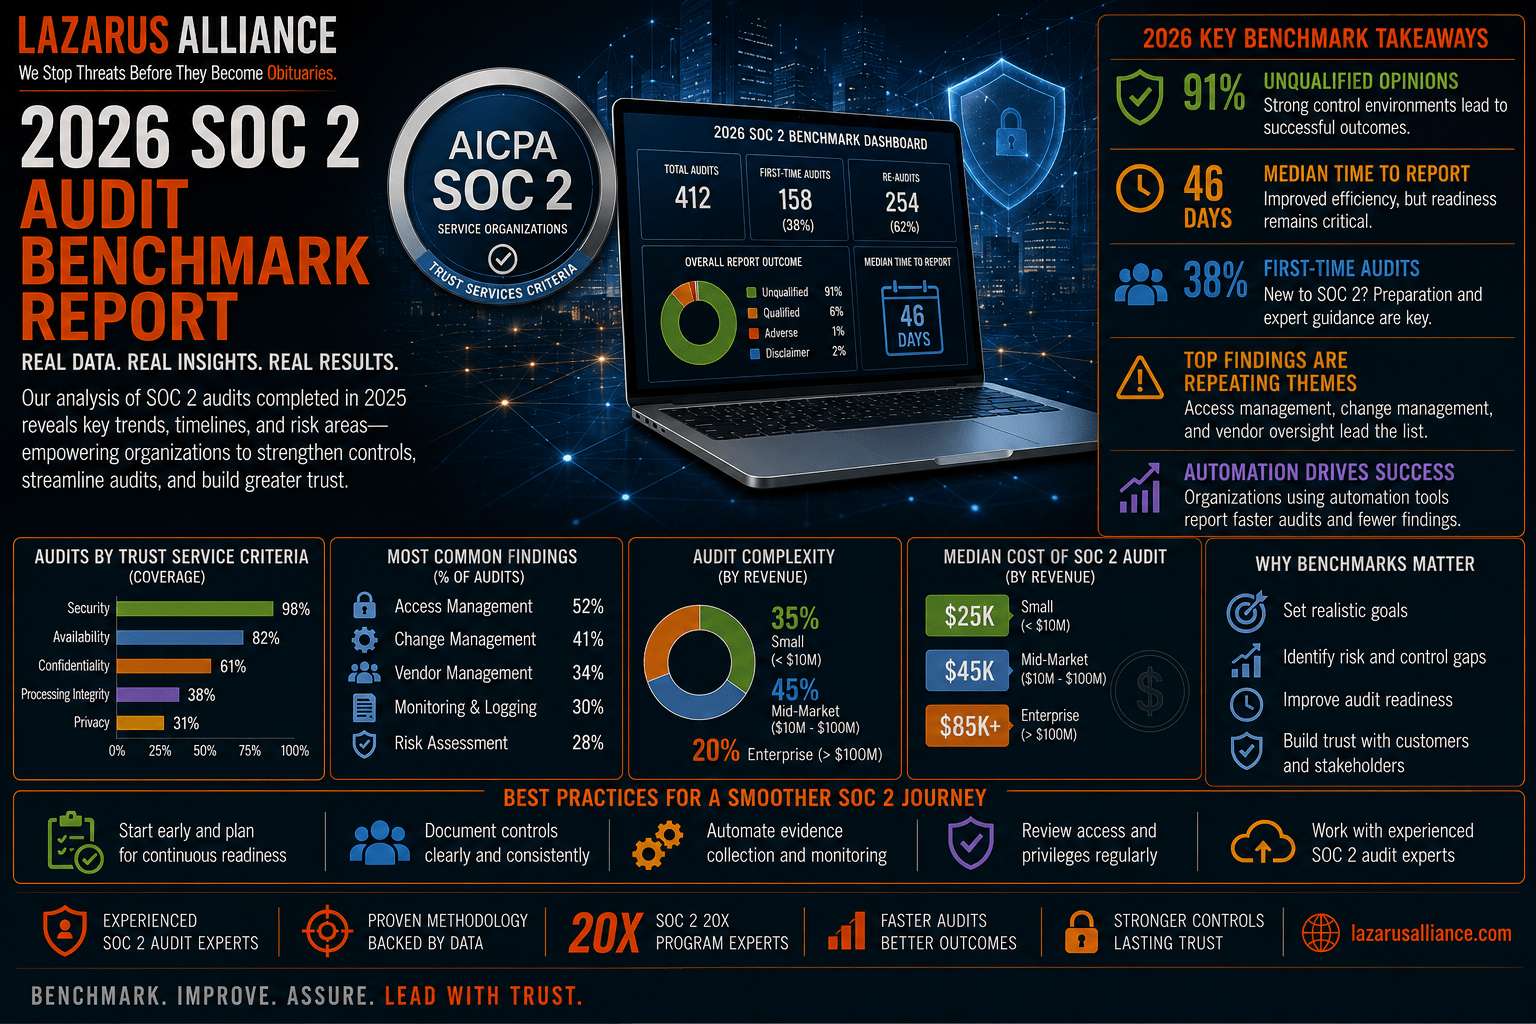
75Completed SOC 2 Assessments Analyzed
2026 SOC 2 Assessment Benchmark Report
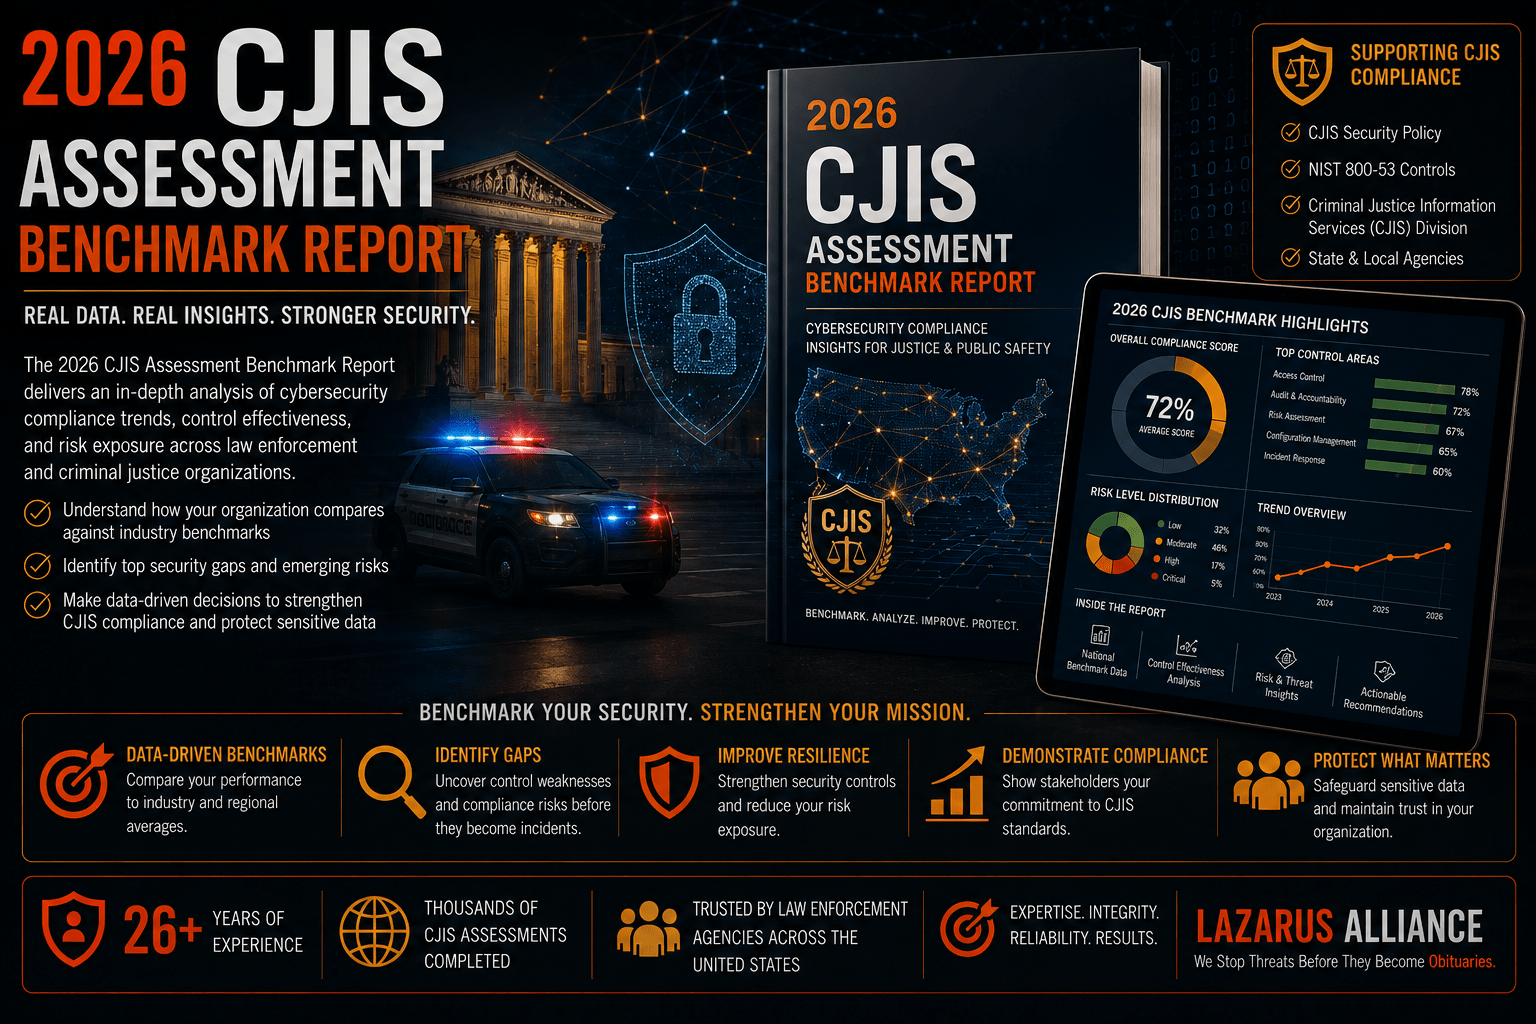
28Completed CJIS Assessments Analyzed
2026 CJIS Assessment Benchmark Report
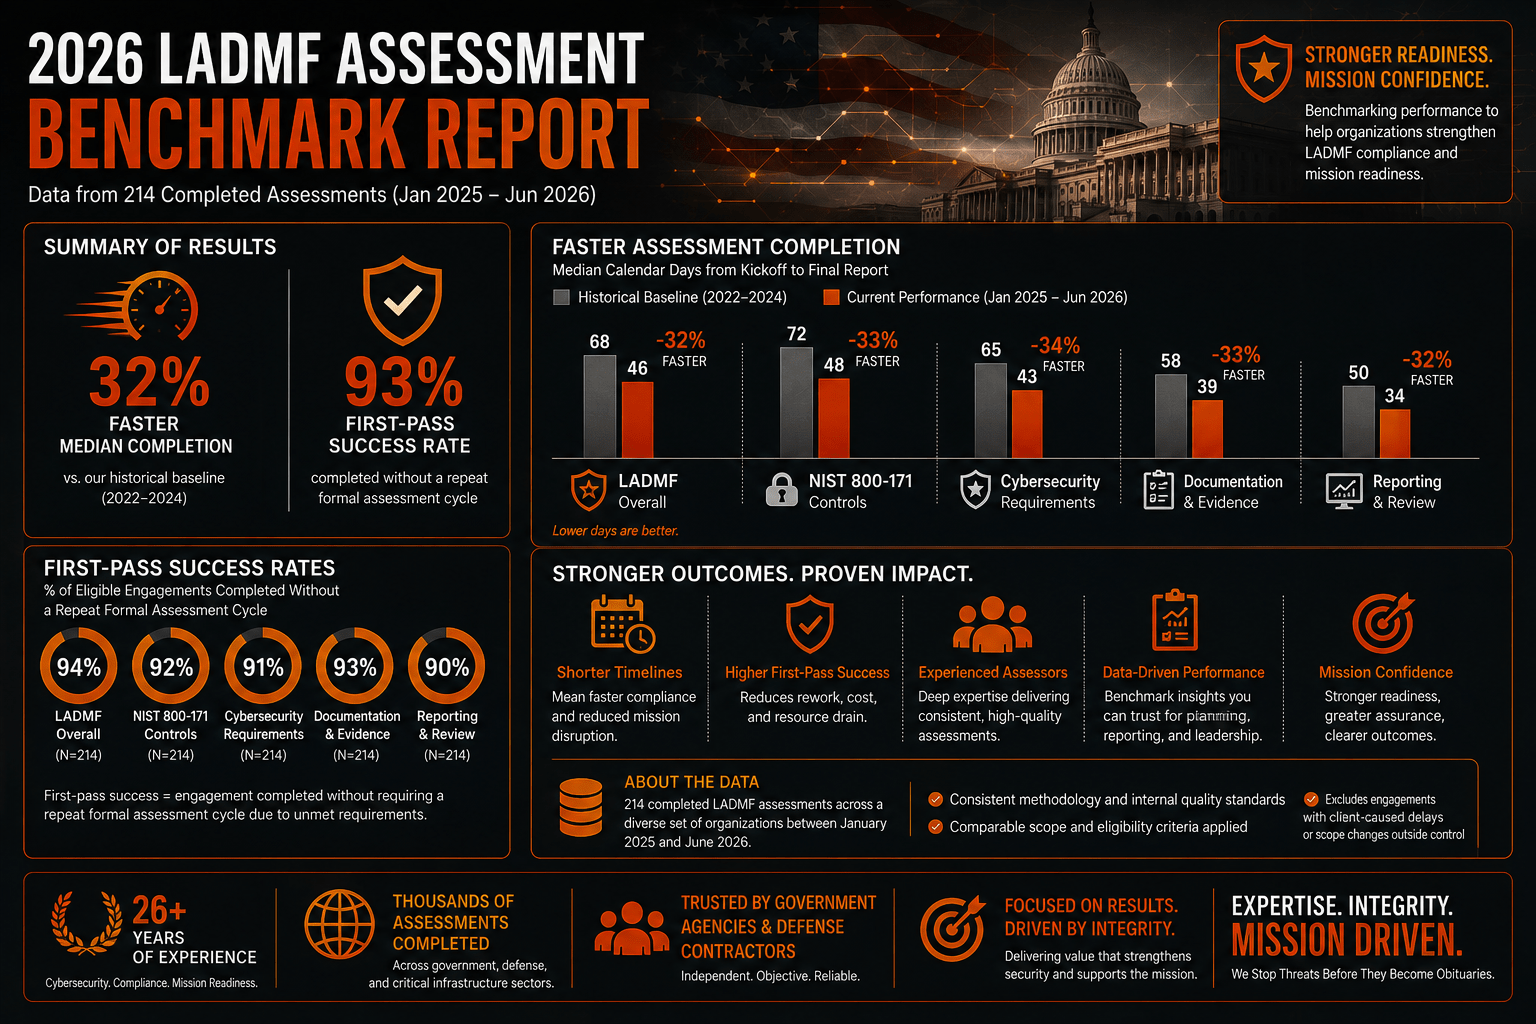
18Completed LADMF Assessments Analyzed
2026 LADMF Assessment Benchmark Report

Explore Lazarus Alliance Research →

Frequently Asked Questions

Lazarus Alliance is a veteran-owned global provider of Proactive Cybersecurity® services. For over 26 years, we have delivered audit, compliance, risk management, privacy, penetration testing, and governance solutions to organizations of all sizes across every industry and jurisdiction.

Proactive Cybersecurity® is our core philosophy of stopping threats before they become problems. We focus on continuous monitoring, real-time risk management, and building sustainable programs instead of reactive “check-the-box” audits.

Lazarus Alliance provides CMMC C3PAO assessments, FedRAMP 3PAO assessments, SOC 2 examinations, PCI DSS QSA audits, risk assessments, privacy impact assessments, vulnerability and penetration testing, policy and governance development, and Cybervisor® advisory services.

Call +1-888-896-7580 or complete the form on this page for a free, no-obligation consultation with one of our expert Cybervisors®.

Lazarus Alliance combines experienced assessment teams with structured evidence workflows and automation designed to improve assessment efficiency and evidence quality. Framework-specific benchmark results are published through Lazarus Alliance Research.

A Cybervisor® is our senior-level, AI-enhanced cybersecurity advisor who works as an extension of your team. They provide strategic guidance, hands-on implementation, and continuous support to accelerate compliance and strengthen your overall security posture.

Yes. We partner with organizations of all sizes, from startups to global enterprises like Cisco and Vanguard, across every major industry. Our efficient methodology makes compliance achievable without unnecessary complexity or cost.

Absolutely. We support clients worldwide with deep expertise in both U.S. and international regulations, including CCPA, PIPEDA, DPDP, and other global privacy and cybersecurity requirements.

Phone consultations: Monday–Friday, 8:00 AM–5:00 PM MST. Form and email inquiries receive a next-business-day response.

Expert Publications

Expert Publications deliver timely cybersecurity insights, regulatory analysis, and practical guidance from Lazarus Alliance experts on emerging threats, compliance requirements, industry developments, and evolving security standards.

CJIS Compliance Renewals: Lazarus Alliance Governance Audits

CJIS Security Policy Audits: Governance and Readiness

Organizations that access, store, process, or transmit Criminal Justice Information must maintain security controls consistent with the FBI Criminal Justice Information Services Security Policy. Effective governance helps organizations assign responsibility, preserve evidence, correct deficiencies, and demonstrate that required safeguards operate as intended.

CJIS compliance should be treated as an ongoing operational responsibility, not a one-time certification or renewal exercise.

Read More

FedRAMP 20x Ready: Lazarus Alliance Compliance Assessments Now

FedRAMP 20x Readiness and Independent Assessments

FedRAMP 20x modernizes federal cloud security certification through measurable security outcomes, persistent verification, machine-readable information, and greater reliance on automation.

The FedRAMP Consolidated Rules for 2026 establish the applicable requirements. Cloud service providers should use those rules, rather than assumptions carried over from legacy FedRAMP processes, to select a certification class and prepare their cloud service offering.

Read More

GovRAMP Expansion: Lazarus Alliance State Cloud Audits

GovRAMP Cloud Security Assessments and Verification

GovRAMP provides a standardized, NIST-aligned framework for evaluating cloud products used by state, local, tribal, territorial, and educational organizations.

The program helps public-sector organizations make risk-based procurement decisions using independently assessed security information. It also gives cloud service providers a reusable way to demonstrate their security posture across participating jurisdictions.

GovRAMP participation does not mean every participating state imposes the same requirement. Each government organization determines which GovRAMP status, impact level, and contractual conditions apply to a particular procurement.

Read More

Awards and Accolades

Do you have any questions?

Lazarus Alliance is the premier global provider of Proactive Cybersecurity®, delivering direct access to top-tier experts in cyberspace law, IT security and operations, risk and governance, compliance, policy development, and related fields.