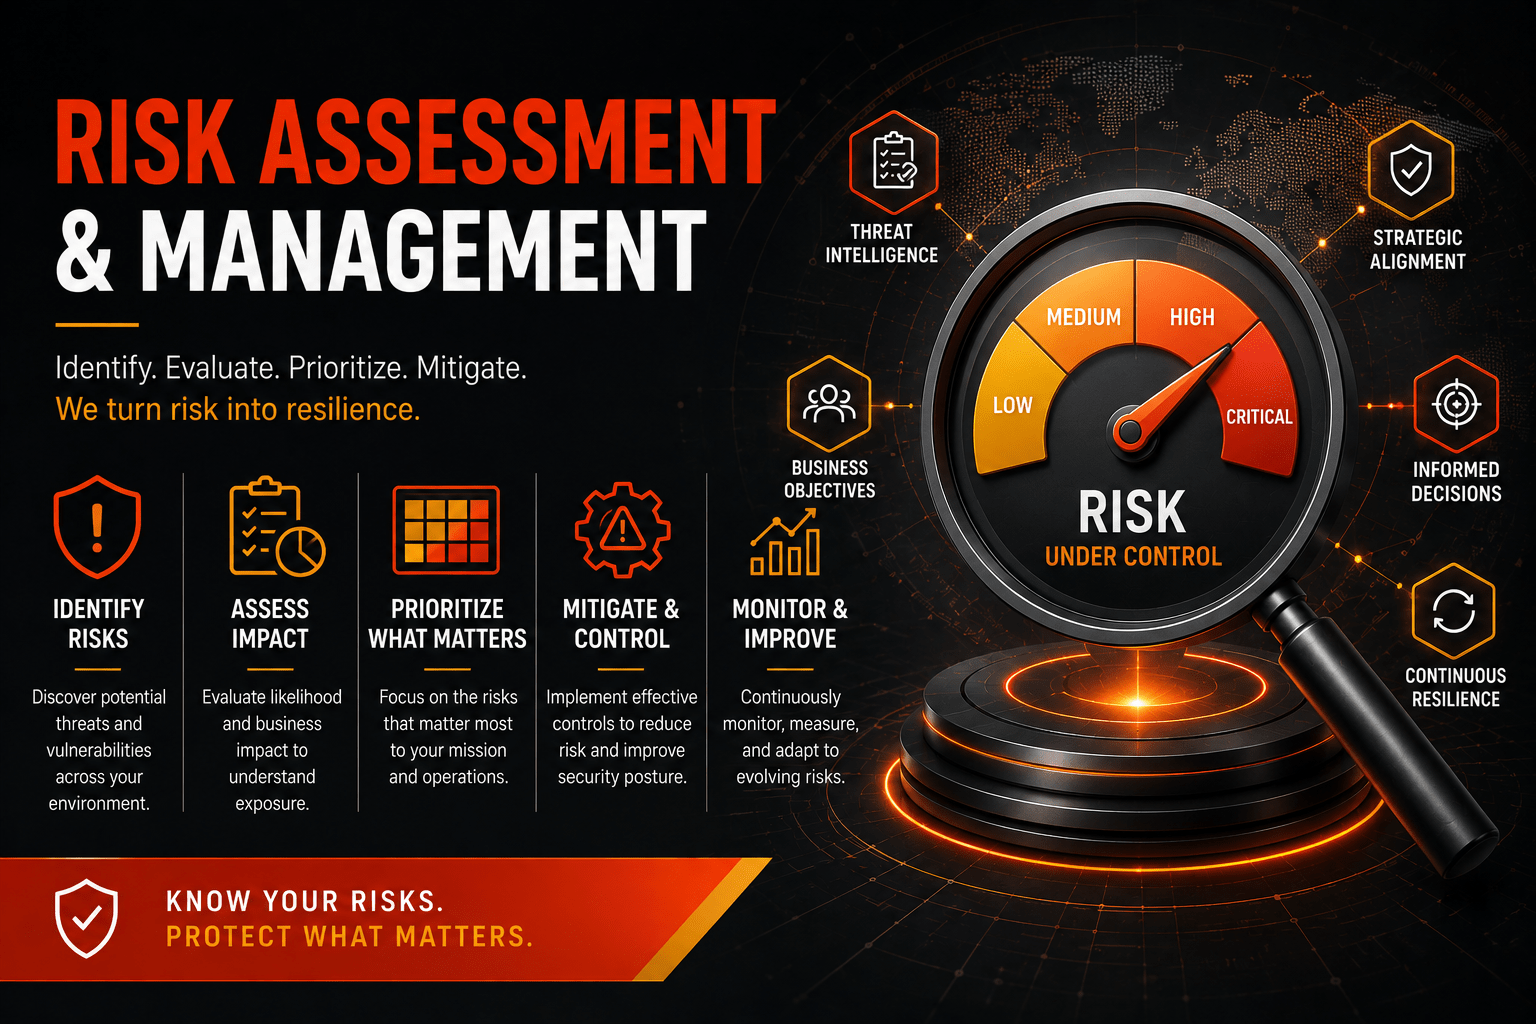
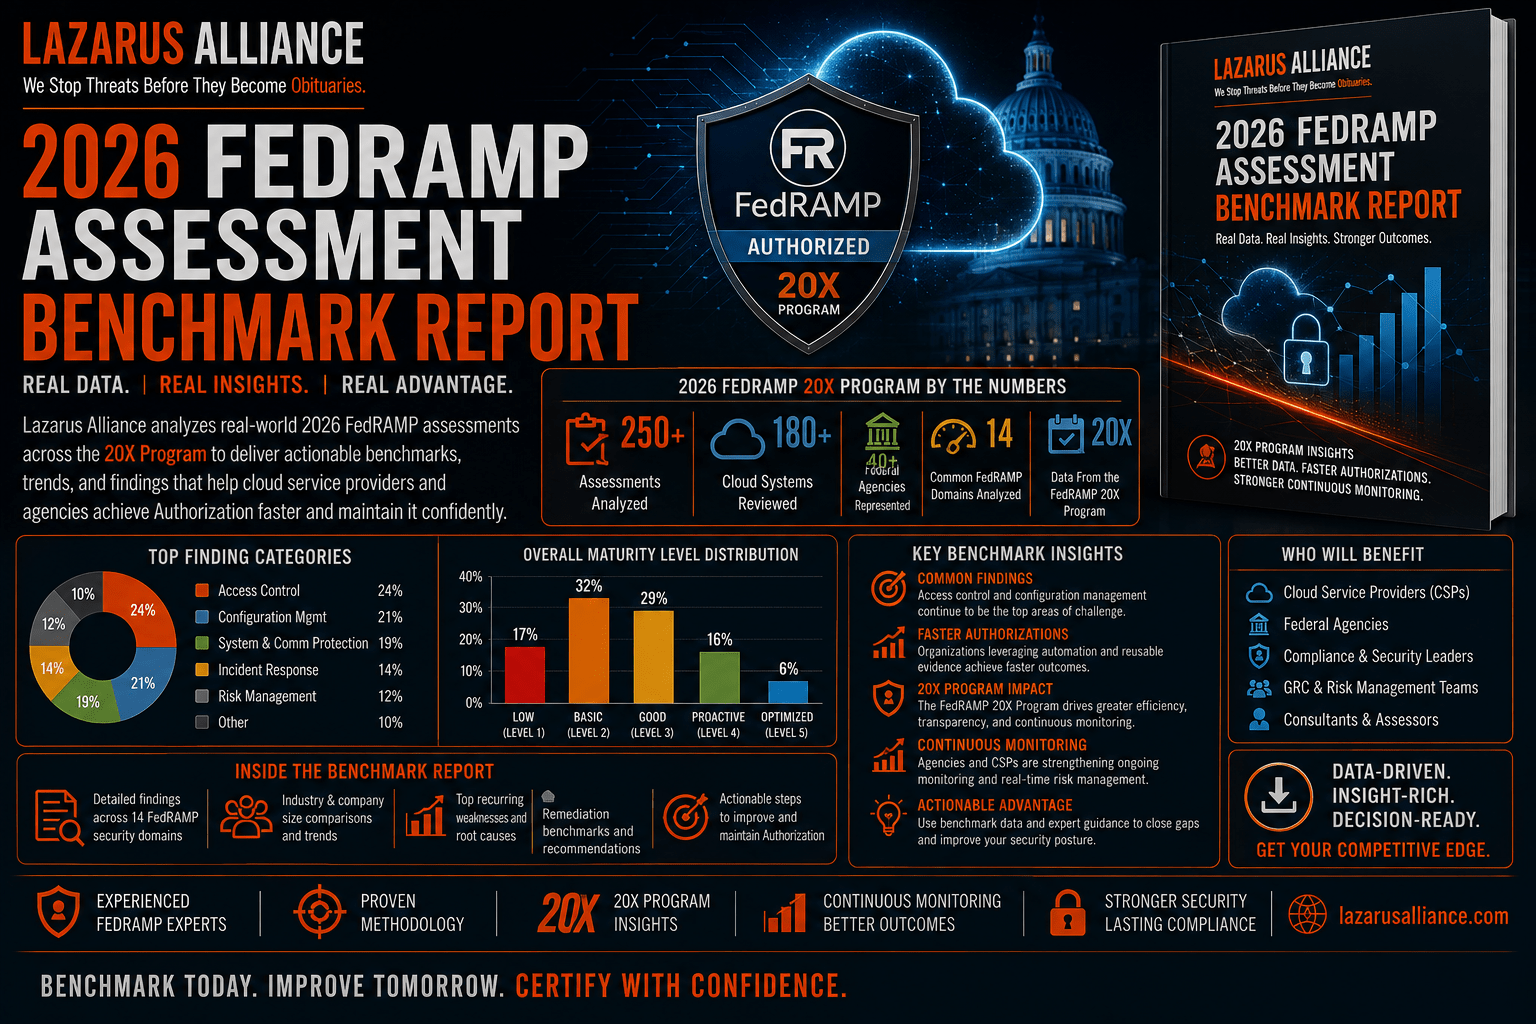
Contrarian view: GovRAMP is not just another badge for cloud vendors. For SLED buyers, it is becoming procurement infrastructure: a way to replace one-off questionnaires with reusable, NIST 800-53-based security assurance that can survive contract review, cyber insurance scrutiny, incident response, and public accountability. The organizations that win in this environment will not treat GovRAMP or StateRAMP as a paperwork exercise; they will engineer auditable cloud operations from architecture through continuous monitoring.
Cybersecurity Audit & Compliance
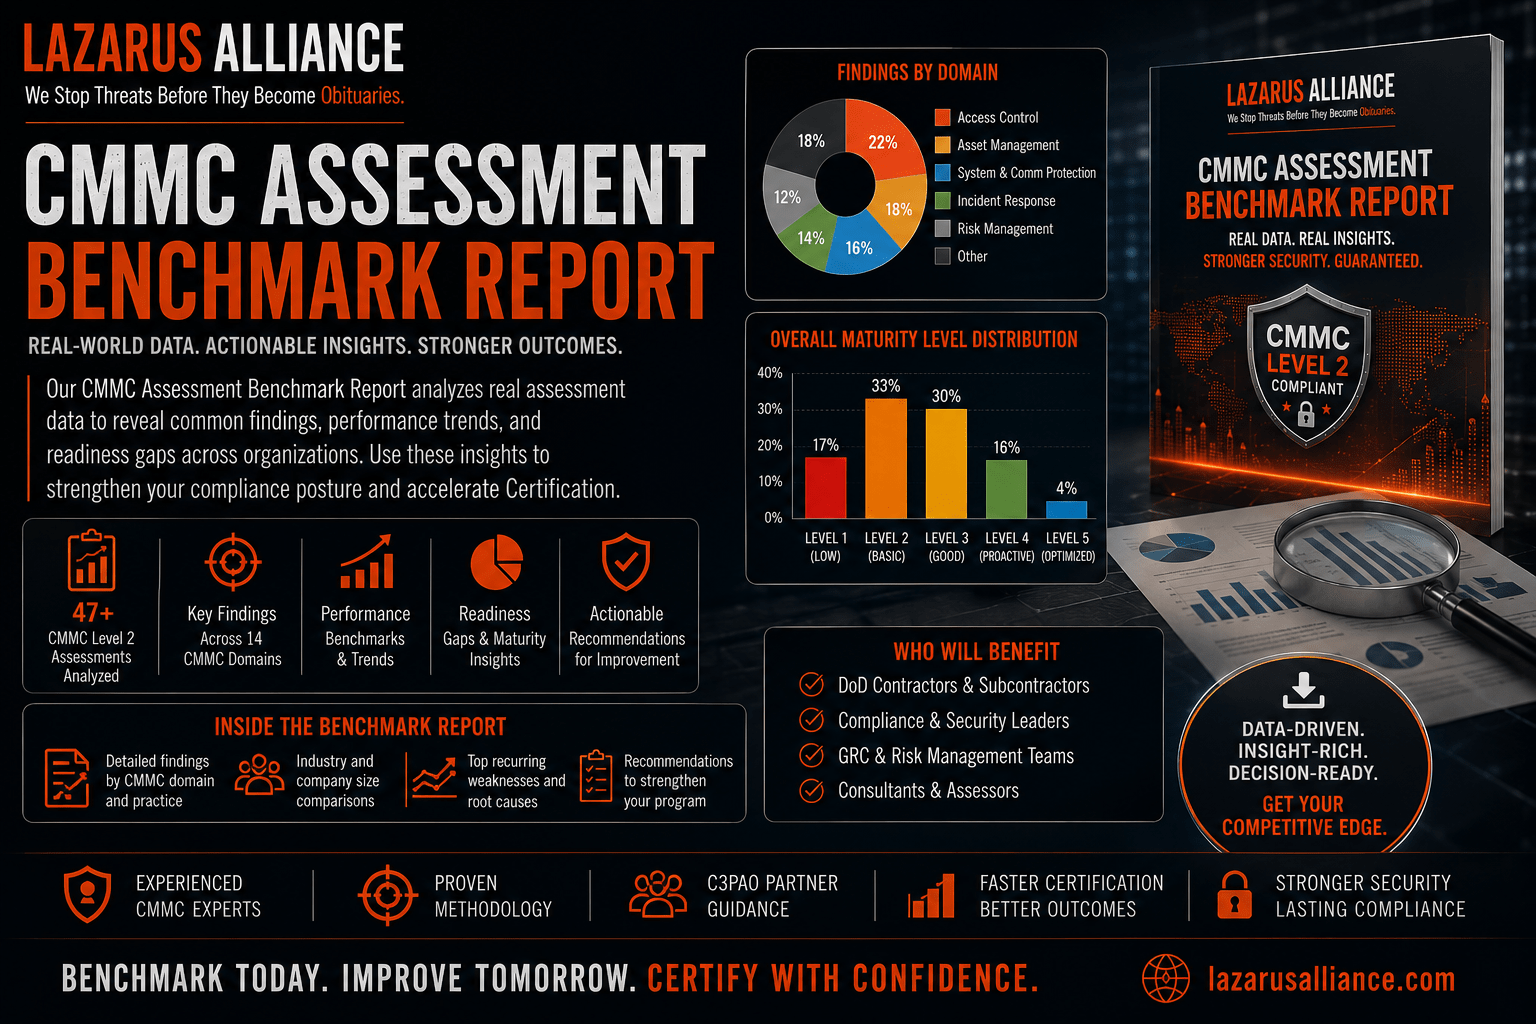
Authorized CMMC C3PAO, FedRAMP 3PAO, SOC 2 & PCI DSS QSA assessments. Independent cybersecurity assessments designed for efficiency, clarity, and defensible compliance outcomes.