



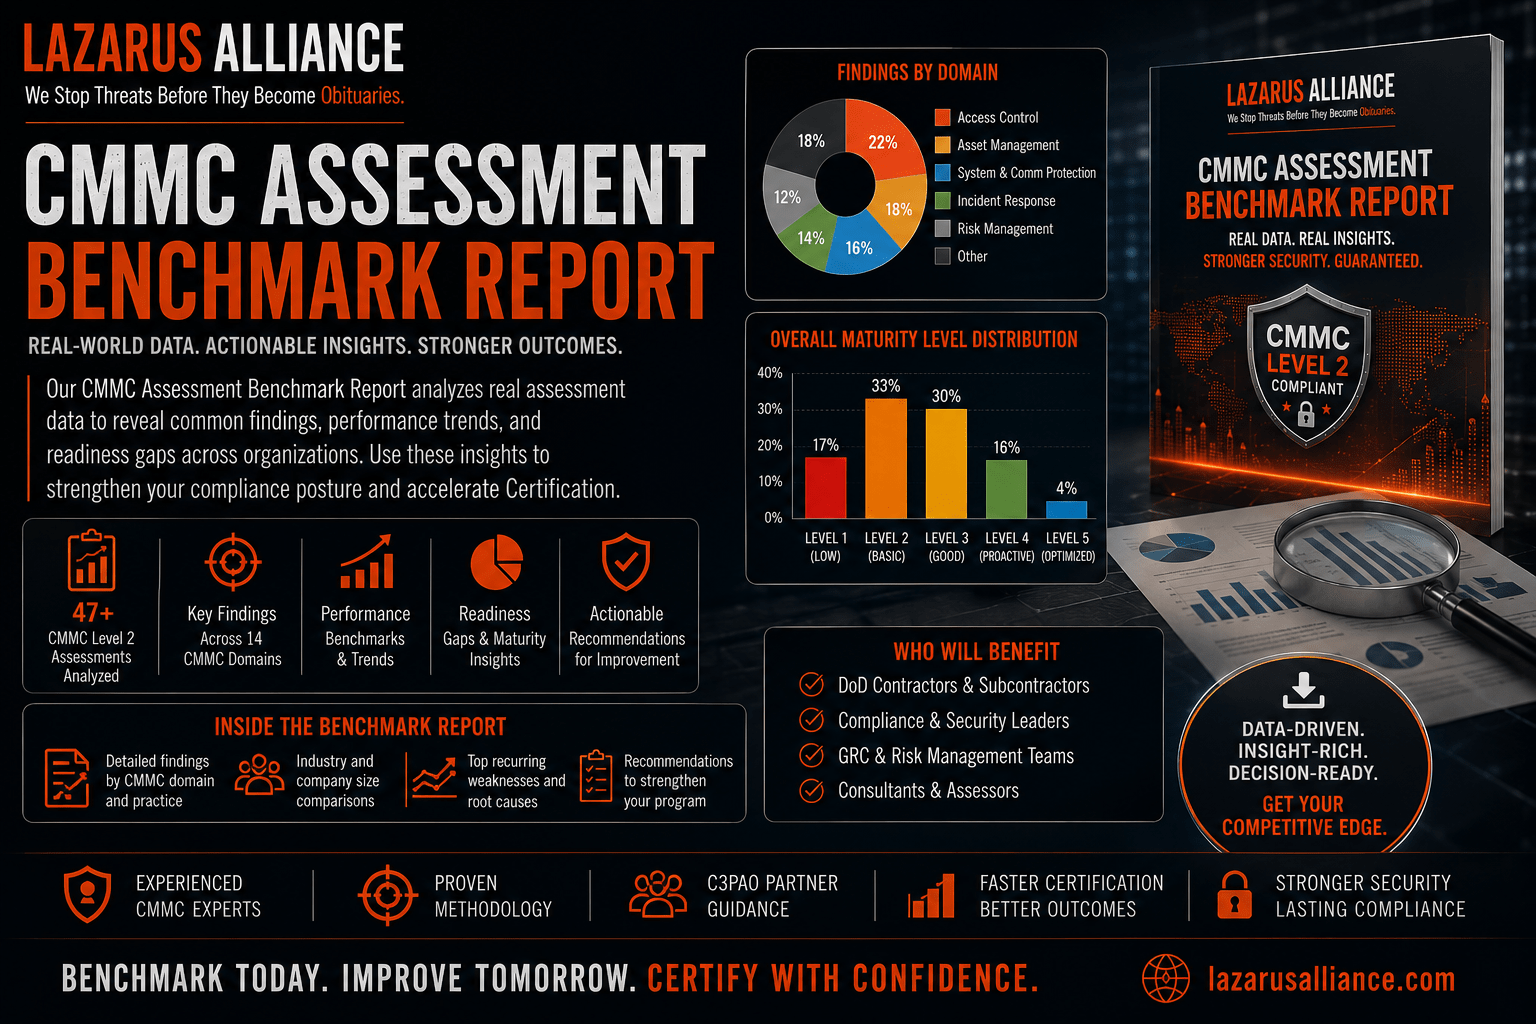
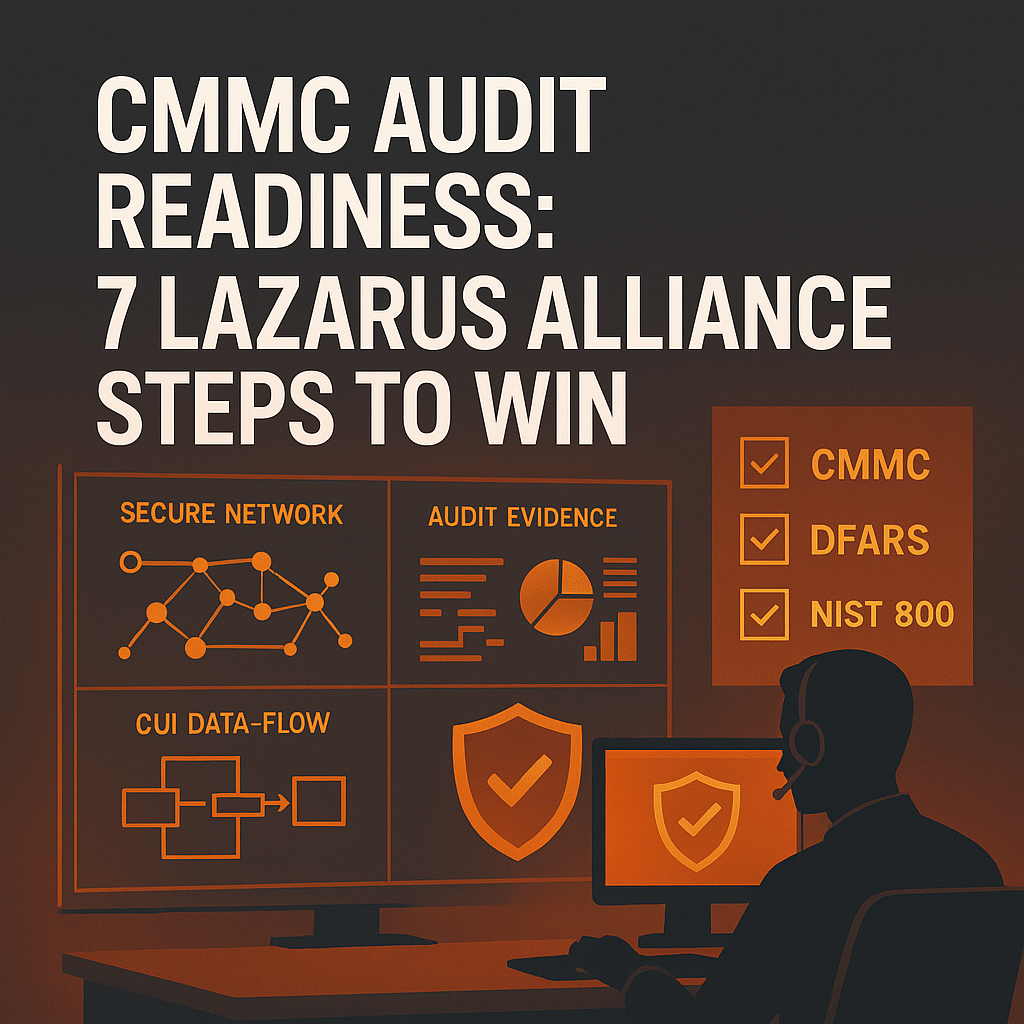
CMMC audit readiness is no longer a paperwork sprint at the end of a capture cycle. For defense contractors, the practical question is now whether cybersecurity evidence is strong enough to protect contract eligibility, survive assessor scrutiny, and support subcontractor flow-down without creating operational drag. The strongest programs treat CMMC and DFARS compliance as a revenue assurance discipline: scope the environment, prove NIST 800-171 implementation, close risk, and maintain audit-ready evidence continuously.

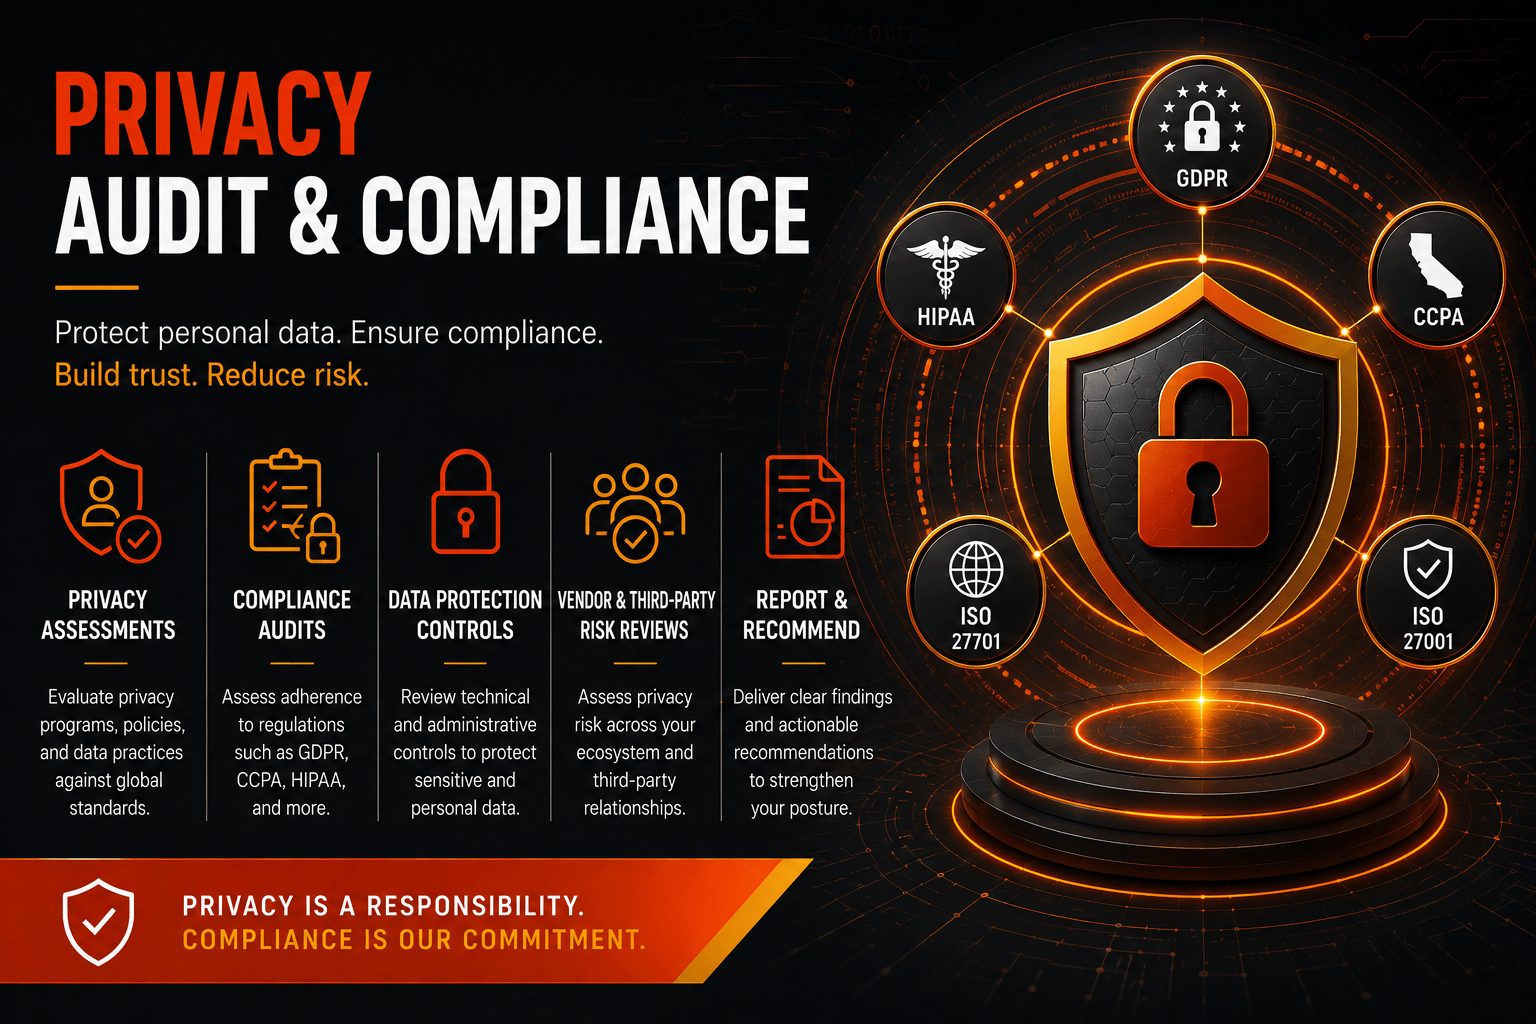
Cybersecurity Audit & Compliance
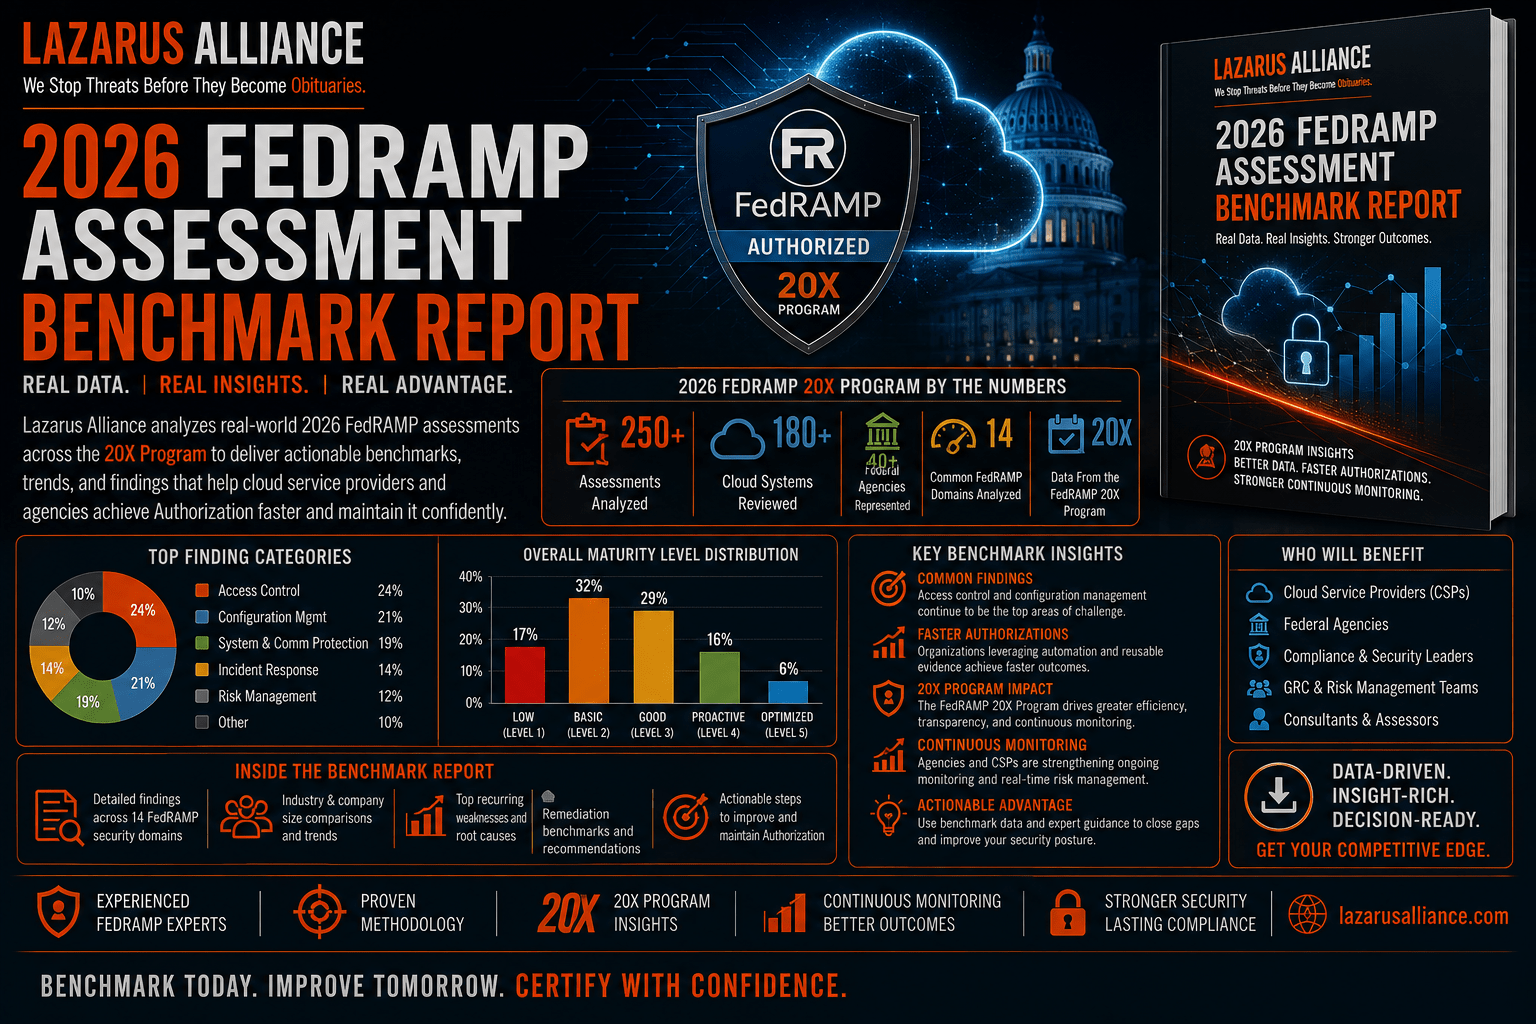
Authorized CMMC C3PAO, FedRAMP 3PAO, SOC 2 & PCI DSS QSA assessments. Independent cybersecurity assessments designed for efficiency, clarity, and defensible compliance outcomes.