




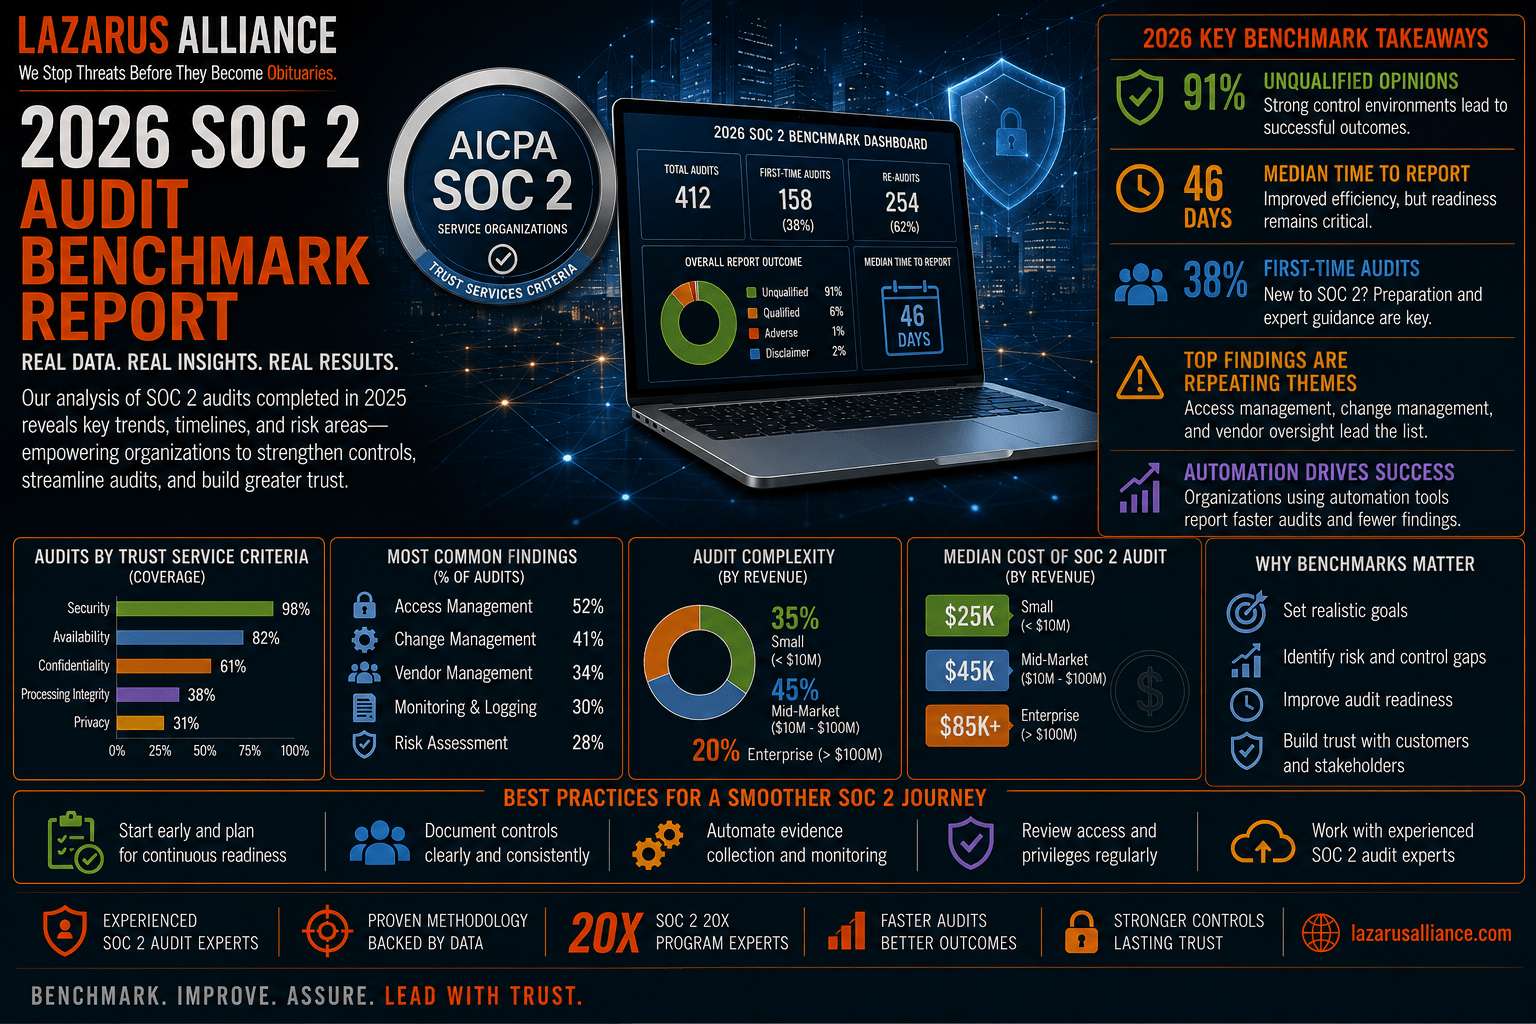
The most important SOC 2 AI governance lesson for 2026 is counterintuitive: waiting for the proposed criteria to become mandatory is itself an audit risk. The AICPA SOC 2 Working Group is seeking public comment on proposed 2027 SOC 2 Trust Services Criteria and Description Criteria, with comments open through Jan. 15, 2027 and an expected effective date for engagements beginning on or after Dec. 31, 2027 if approved, with early adoption permitted AICPA & CIMA, SOC Suite of Services. The proposed modernization addresses AI governance, model monitoring, prompt manipulation, data poisoning, AI-output transparency, training data management, and automated decision-making CPA Practice Advisor, AICPA Proposes SOC 2 Trust Services Criteria Update.
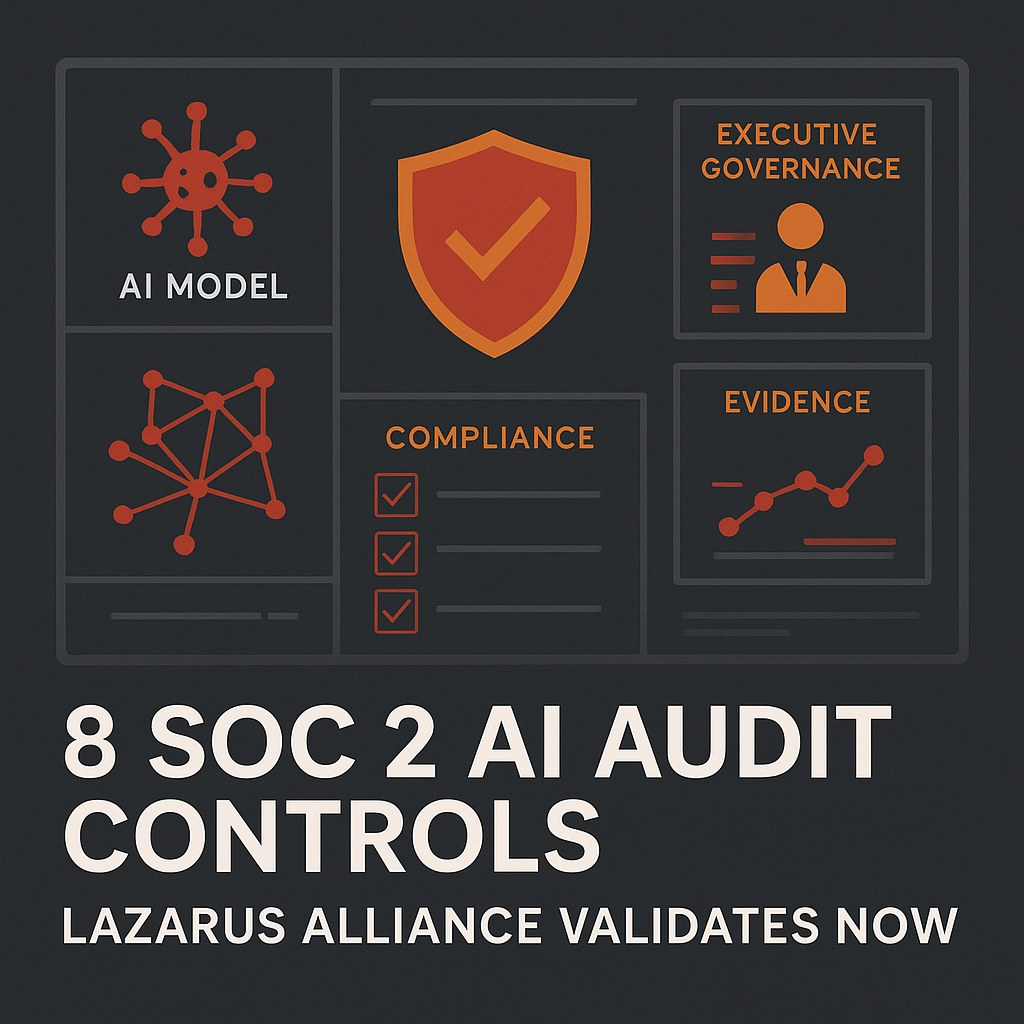
For service organizations, that means SOC readiness can no longer treat artificial intelligence as a side project owned only by product teams. AI now affects the system description, control environment, risk assessment, change management, third-party risk, privacy, incident response, and monitoring evidence that auditors evaluate in a SOC 2 audit. Lazarus Alliance validates these controls now because customers, boards, underwriters, and regulators are already asking for AI assurance before the proposed criteria become effective.