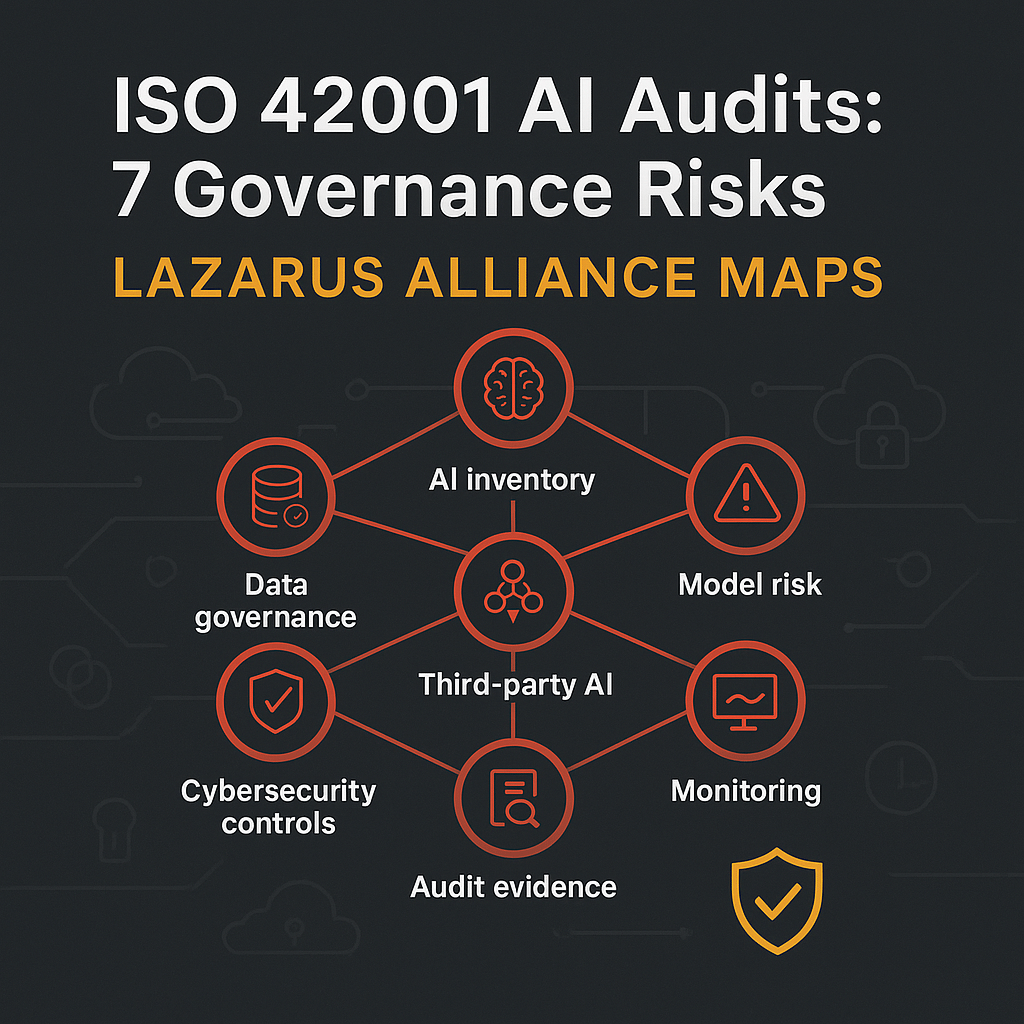
ISO 42001 AI Audits: 7 Governance Risks Lazarus Alliance Maps

ISO 42001 AI Audits: 7 Governance Risks Lazarus Alliance Maps

AI audit readiness is no longer a documentation exercise. The organizations that will pass an ISO 42001 AI governance audit with confidence are not the ones that merely publish an AI policy; they are the ones that can prove, with evidence, that AI risks are identified, assigned, tested, monitored, escalated, and improved through the same disciplined governance expected in mature cybersecurity audits and compliance assessments.

That distinction matters because ISO/IEC 42001 establishes requirements for an artificial intelligence management system, while the NIST AI Risk Management Framework organizes AI risk work around governance, mapping, measurement, and management activities ISO, ISO/IEC 42001 NIST, AI Risk Management Framework. In practice, an AI governance audit must connect board oversight, model risk, cybersecurity, privacy, third-party risk, incident response, and control evidence into one defensible assurance story.

Lazarus Alliance maps ISO 42001 audit readiness through the lens of enterprise assurance: what is in scope, what can fail, what evidence proves control operation, and where AI risk intersects with cybersecurity audits, SOC reporting, FedRAMP-style evidence discipline, HIPAA safeguards, PCI DSS obligations, CMMC and DFARS requirements, CJIS expectations, IRS 1075 controls, C5 cloud criteria, ISO 27001, and the LA DMF ecosystem. The result is not a generic AI checklist. It is a governance-risk map designed for CISOs, compliance officers, legal teams, product leaders, and audit committees that need assurance before customers, regulators, or examiners ask harder questions.
Read More

SOC 2 Audits: 8 Cloud and AI Risks Lazarus Alliance Tests

SOC 2 Audits: 8 Cloud and AI Risks Lazarus Alliance Tests

The most difficult SOC 2 audit findings in 2026 are rarely caused by a missing policy. They usually come from an inaccurate system boundary: a cloud service outside the diagram, an AI workflow nobody classified, a subservice organization omitted from the description, or monitoring evidence that exists but cannot be tied to the in-scope system. For organizations pursuing a SOC 2 audit, SOC 1 readiness, cloud compliance, AI governance, or broader cybersecurity audits, the strategic question is no longer simply, Do we have controls? It is, Can we prove the right controls operated over the right system, for the right period, with the right third-party dependencies disclosed?

Read More

Third-Party Risk Audits: 10 M&A GRC Checks With Lazarus Alliance

Third-Party Risk Audits: 10 M&A GRC Checks With Lazarus Alliance

In M&A cybersecurity due diligence, the most dangerous finding is not always an unpatched firewall, a missing SOC 2 report, or an overdue policy review. The larger risk is often a false sense of assurance created by questionnaires that never test whether controls actually operate under stress. A third-party risk audit should therefore answer a deal question: will this target, vendor, or portfolio company introduce material cyber exposure, regulatory liability, ransomware risk, or AI security risk after close?

That question has become urgent. Verizon reports that its 2026 Data Breach Investigations Report analyzed more than 22,000 confirmed breaches, found vulnerability exploitation in 31% of breaches with known initial access, ransomware in 48% of breaches, and third-party involvement in 48% of breaches Verizon, 2026 Data Breach Investigations Report. IBM also reports that enterprise security incidents increasingly involve AI models or applications, and identifies prompt injection, data poisoning, data leakage, model inversion, and shadow AI as AI workload threats IBM, What is AI Workload Security?.

Lazarus Alliance approaches M&A cybersecurity due diligence as an evidence-based GRC audit, not a paperwork exercise. The following 10 GRC checks help boards, private equity sponsors, CISOs, general counsel, compliance officers, and IT directors evaluate acquisition targets and critical vendors before cyber risk becomes enterprise risk.

Read More